Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Archive for the ‘Personal’ Category

4 Actions Needed Now From City of London Police and Action Fraud

Summary: The investigation of Sirius ‘Open Source’ and any remedial actions for the crimes committed

  1. The perpetrators of the fraud all need to be held accountable. This may also mean extradition and arrests. Several people were aware if not directly involved, possibly not limited to Sirius management but also the IFA and the accountants (without their active or passive cooperation it would not work; they legitimised this fraud).
  2. The money which got stolen from all the staff needs to be recovered; it is expected the company will claim that there’s no money left, having emptied accounts and maybe hid the money somewhere far away, maybe under other people’s names, possibly in anticipation of the fallout as soon as victims find out. This step may require subpoenas (to unveil the list of victims, then get in touch to inform them one by one).
  3. Compensation to Rianne and myself, as we were both workers who were mistreated on numerous different grounds (as above, the company may pretend that it cannot afford this). Financial accountability for this elaborate embezzlement can be passed outwards as deep-pocketed facilitators existed*.
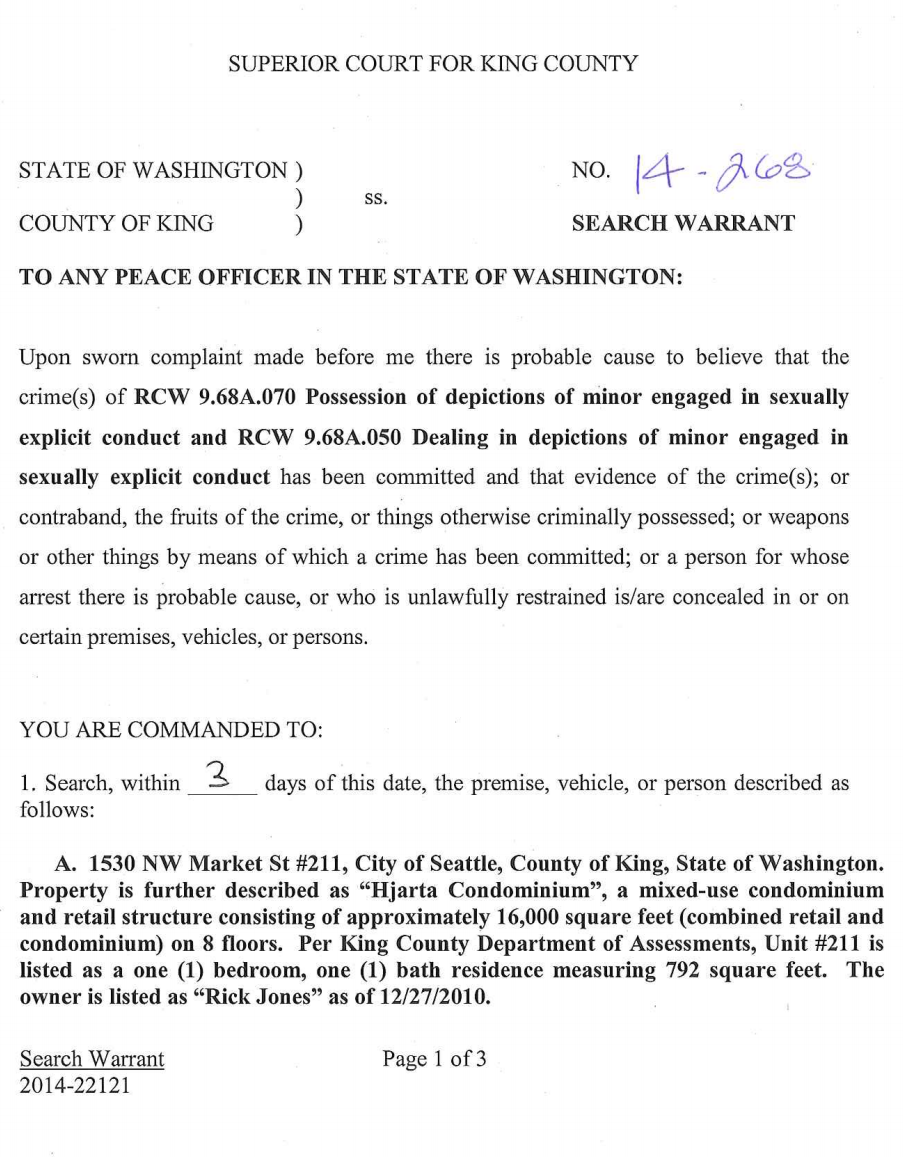
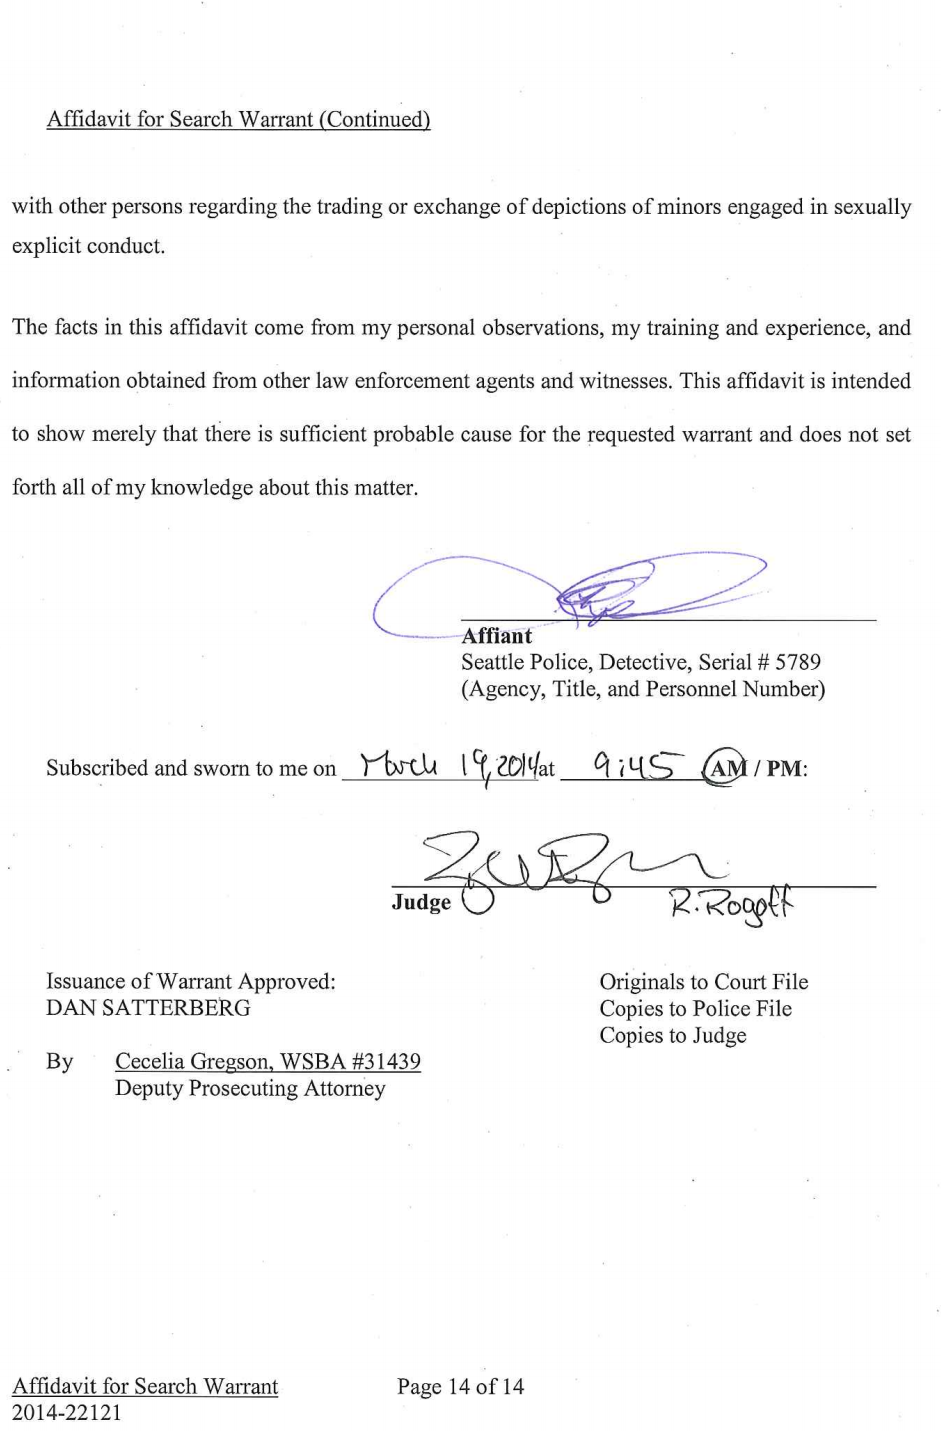
  4. Unseal the non-disclosure agreement signed with the Gates Foundation in 2019. The timing suggests a correlation with sham staff contracts and two new shell companies, one in Washington State, not far from the Gates Foundation; this also coincided with Techrights pursuing nearly 3,000 pages from police in Washington State — those pages were eventually received from Seattle police* and did in fact confirm an arrest for pedophilia at the home of Bill and Melinda Gates.

______
* It is our knowledge and understanding that the company began hiding behind its accountant (I confronted the CEO about the change of address over the telephone — a very long phonecall — this past October or a day after it had happened). The company has an address at the heart and centre of London. Even its shell has the same address in London. We understand that the City of London Police is now involved (we’ve receive formal communications from the City of London Police) and we’ve also heard from someone who reckons the wheels are in motion at the police, for reasons we shall cover in the future. The City of London Police does have the powers to locate and apprehend these people. I am just a citizen, I’m not a cop, and I’ve asked the police since March to take action (this weekend is July already). There are many victims here, not just me. Noticed we’ve all along refrained from naming the perpetrators because we don’t know how many of them there are and we don’t want to falsely accuse those who are merely suspects.

** Case Investigation Report: 2014-22121 (Seattle Police Dept. [1, 2])

One Month of Police Silence: Where is Accountability?

Video download link | md5sum 0de07faab93ab5373d58e77a04fca707
The MP Comes Marching in
Creative Commons Attribution-No Derivative Works 4.0

Summary: The pension fraud at Sirius ‘Open Source’ (committed against programmers and sysadmins focused on GNU/Linux and Free software) has reached the political level; so far one can observe that politicians aren’t quite in control of the police or, contrariwise, the police enjoys immunity or exercises impunity because it simply doesn’t bother responding to politicians

A MONTH ago I turned to my Member of Parliament (MP) after the police had failed to look into fraud complaints (myself and colleagues, GNU/Linux sysadmins for the most part, were victims). My MP’s office said 4 weeks should be more than enough for police to respond, but nothing has happened, so today I disclose what happened and what will happen next (it’s far, far from over).

The video above gives a rough introduction to the issue, which is moreover explained succinctly below. When I contacted my Manchester MP a month ago I said:

Dear ????? ???????,

My name is Roy and I live in Manchester. My employer, which I resigned from in December, turned out to have engaged in embezzlement against me for over 5 years. It was pension fraud. My “pension” money was never given to a pension provider as the payslips said, and instead went into the management (black hole). Upon further inquiry this was confirmed by formal letters and I discovered they did the same to my colleagues. I reported this to Greater Manchester Police, which insisted that I file a case with Action Fraud. After 4 weeks of waiting Action Fraud made is abundantly clear that it did not even look into the case. It just turned away victims. According to media reports in reputable sources, this is quite common. I reach out to you as this is a severe political blunder at this point. I chronicled some of this in http://techrights.org/wiki/Sirius_Open_Source and http://techrights.org/wiki/Crimes_of_Sirius_Open_Source though it seems actual enforcement — something only the police can do — is needed now. Will you please bring up this matter or help me pursue justice not just for myself but also my colleagues?

Yours sincerely,

A lot of time has passed, a lot of messages were exchanged, but no progress could be made because the police is “MIA”. (Missing In Action)

Ironically, they call themselves Action Fraud. According to British broadcasters, they’re notorious for not taking action. Sure, they take reports. They have bots to respond to the reports, but what good are bots?

The ‘My “pension”‘ sentence (above) could be further elucidated. It might lead with the fact that the company withdrew money from paychecks under the pretence of contributing to the fund but never actually did so. The current wording could be made more clear. “As for turning away victims,” one person noted, “ensure that it is clear that there are many of your former colleagues in the mess as well. The closing line is quite clear, which is important.”

In the next part I’ll share some more correspondence from and to the MP. What we strive to show now is that there’s no system of accountability or, if such a system does exist, it’s clearly not functioning. It fails victims and rewards criminals.

Looking Back at Crimes of Sirius ‘Open Source’, Aside From Moral Depravity

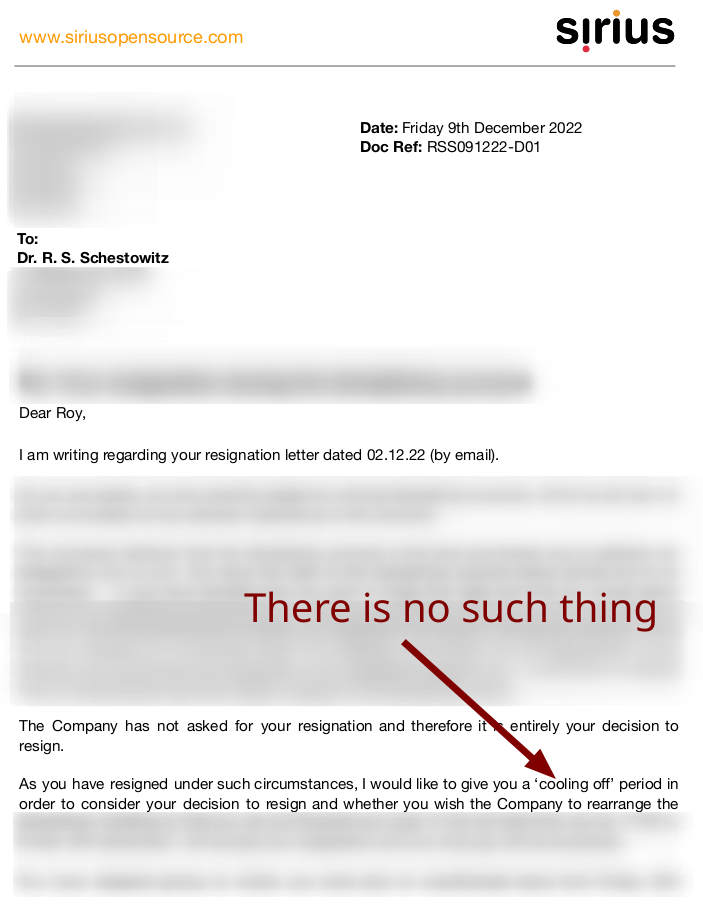
Roy's resignation page 1: There is no such thing; Nothing was paid; they had us sign another; a decade out of date; Those terms are clearly applicable only while employed; stuff inapplicable after departure; It is not defamatory if it's true and honest; you are not my boss; The Company does that on its own

Summary: Six months ago Sirius ‘Open Source’ had the audacity to tell people whom it robbed that they need to “cool off” (no such obligation); imagine a rapist telling the victim to just “chill”; today we revisit the matter

THE departure from Sirius half a year ago was long overdue. The company had done a number of bad things other than the pension fraud (which we didn’t know about at the time; there were mere suspicions). At one point I even considered leaving abruptly, seeing how colleagues were being treated/mistreated. One of them got diarrhea from the stress. He was routinely and casually bullied by fake ‘managers’. I had enumerated clients I was not happy about and discussed it privately with friends. It’s my legal right. I can talk about work (though this was not at all mentioned internally; I had kept these 100% to myself and only Rianne knows the full reasons for disdain because she worked in the same company).

Where does one even start describing what went on in the company? First there’s Bill Gates: notorious, corrupt, working in the shadows and perhaps passing a bribe? I never ever had any contact with that (perhaps LDAP) project, but that still reeks/stinks a lot. Why was there an NDA and why would an American approach a British company? The one that employs a Gates critics who is pursing police files about Gates at the time. It’s not like Microsoft did not already try this. It tried contacting the same company, explicitly complaining about me. Some other day I’ll elaborate some more on that. It’s another kind of bullying.

Then we had this public sector client that was also connected to Microsoft; well, they moved from Windows to GNU/Linux but stayed on Azure; thankfully I never even logged in to that crap (but one day they MIGHT ask me, or so I worried, and then what?). For another client there was an Amazon/AWS migration planned (used to be a domestic company doing the hosting); more AWS is not the ‘skill’ we want to develop, is it? By 2022 there 3 more “problematic” clients: some Army-connected thing (US), a loan shark, a company that employs criminals and us acting as secretaries of theirs, picking up fault reports, not even solving them. What was happening to Sirius? As I noted the day I left the company, at one point that year I was even asked to look at server logs for an anti-abortion group. Was the twice-divorced CEO becoming a misogynist, too?

The irony is that the CEO kept bragging about me working for the company, using that to recruit people (those people told me that). And after he defrauded me and my colleagues (some of them friends) he had the audacity to assert the victims were in fact the problem.

It’s hard to believe it has been this long, but it took about 3 months just to get to the bottom of the pension fraud (with Standard Life openly admitting it in writing). Sure, it’s bad publicity for them if it drags on for months and months, but that’s not the point. It’s just a really slow process and the Sirius scandal will deepen. It will expose and implicate the state, too. Just because Sirius was a contractor and state agencies were “clients” doesn’t mean that the state had no responsibilities and obligations. We suppose this is becoming an epic liability scandal and that’s why they keep so quiet about it. They hope the victims will just forget about it or “move on” out of sheer desperation.

We have a lot left to say; if it were not for source protection, it would boil over completely by now (but possibly burn some innocent people). We’ve heard from journalists, ex staff, applicants, clients… they’re really unhappy about what’s happening in Sirius right now. And just wait, there’s lots more to come.

British Government May Be Indirectly Liable for Fraud at Sirius ‘Open Source’

Video download link | md5sum f4f239686d76f30d562cc44bb70cb997
Serious Scandal by Sirius
Creative Commons Attribution-No Derivative Works 4.0

Summary: What started as fraud committed by one company (since 2011 if not earlier) is becoming a blunder and major embarrassment to high-profile clients that are government agencies, in effect employing programmers and system administrators via a contractor that grossly underpays workers while secretly defrauding them (stealing money from them)

THE previous part spoke of the brain drain that had reduced Sirius ‘Open Source’ to almost nothing; even before pension fraud was exposed (we broke the story here this past spring) the company had almost nothing left in terms of physical assets, monetary assets, human resources, and clients. It’s just milking what’s left of contracts signed or renewed last year.

The really obnoxious thing is the two-faceted ‘coverup’ (to use the term loosely) by entities that should know better and should do better. If the British authorities are so desperate to save face and spare themselves negative publicity, then they should hurry up and act, showing strength of law, accountability, and drastic consequences. Instead, based on the lack of interaction (also my Member of Parliament is being ignored), it certainly seems like this scandal will just deepen, implicating a growing network of facilitators and enablers. This scandal isn’t about just Sirius anymore; Sirius received millions of pounds from the British government and the government oughtn’t look the other way when people who worked on government computer systems become victims of employment crimes and embezzlement or just plain old fraud.

Sirius ‘Open Source’ Far Smaller Than It Wants People to Believe

Summary: Today’s part talks about what’s left of Sirius ‘Open Source’; about two thirds of the people listed in the “Meet The Team” page of Sirius ‘Open Source’ aren’t there (some left years ago), the company is unable to recruit, and LinkedIn is linking the company to people who don’t work (or barely ever work) for Sirius ‘Open Source’

THE pension fraud at Sirius ‘Open Source’ is still being ignored by Action Fraud. This won’t end well because Sirius ‘Open Source’ is connected to Action Fraud through its likely biggest client (if it’s still a client at all). Are they waiting for the company to simply vanish as a legal entity with the word “LIMITED” added to its name, leaving the culprits off the hook? Because it would contribute to the perception that the police becomes an actual facilitator of the crime, for self-serving purposes at least.

We’ve meanwhile noticed that Sirius ‘Open Source’ makes itself look bigger than it really is. Here’s an example:

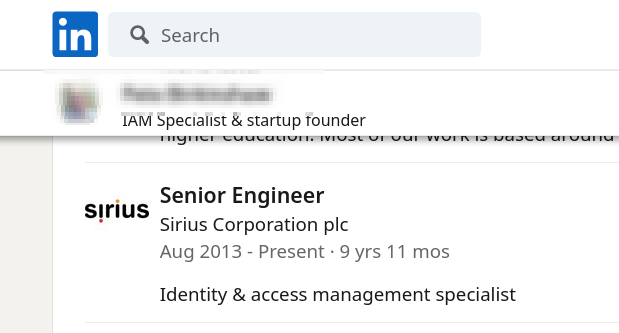
 Sirius 'Open Source' senior engineer

Sirius ‘Open Source’ has maybe paid him for hundreds of hours of contract work over the past decade. That’s a few dozens of hours per year. Don’t be fooled by Microsoft’s LinkedIn. It helps companies, not just people, craft a fictional image/perception of themselves.

British Government Not Investigating and Punishing for Crimes Committed by Its Contractors

Video download link | md5sum 0cf753fb90aab5992efe0bfd625e24fb
Political Escalation
Creative Commons Attribution-No Derivative Works 4.0

Summary: Today’s video mostly covers part 3 of the series while stressing the relevance to Free software and the British government; Sirius ‘Open Source’ did play a big role in adoption of Free software in the UK, so its crimes against staff (that worked on government computer systems) matter a lot, except the British police prefers to overlook this matter

THE pension fraud at Sirius was a serious crimes and the perpetrators of the crime have not been punished yet. For context, this is a company that once upon a time sponsored the Free Software Foundation (FSF) for several consecutive years and wasn’t reluctant to put GNU logos in its Web site.

Things soured over the years. A decade ago I went to a meeting which helped secure a very important deal for the company. I’d rather not name the client, but let’s just say it supervises (or is in charge of) the people who run Action Fraud — basically the very same folks who turned down my report of a crime, a crime committed not only against myself. This is confirmed, it’s not merely a suspicion.

Action Fraud, what about action? Where’s Action Fraud?

Are they trying to hide something?

It has been three weeks already and they’re not even responding to my elected representative, who (to her credit!) seems eager to get to the bottom of it.

The video above is a verbal update on the issue. We still have a lot of material left to publish and many steps remaining to explore, bodies to escalate to, issues to scrutinise etc. This cannot possibly end well unless the perpetrators are held accountable. All of them. Facilitators are another matter as they’re only indirectly culpable. ?

Sirius ‘Open Source’ and a Lack of Accountability in the British System

Summary: Sirius ‘Open Source’ scandals have opened a can of worms; why isn’t a government contractor being held accountable for crimes committed against its staff?

THE company that once upon a time sponsored the Free Software Foundation (FSF and KDE among other things) might cease to exist any day now. In the previous part (with video) of this mini-series we argued that, based on the hard evidence, Sirius loses staff and clients rapidly. There’s almost nobody to actually run what’s left of the company. If the company tries to recruit people, they lack the interest. We have evidence of this too.

Tomorrow morning we’ll release a video to explain how British police is failing to respond not only to reports of a crime but also messages from British MPs. This will lead to further escalations that generally embarrass the system and there’s room for suspicion that the “Establishment” (government) is using one hand to wash the other and in turn wash the face.

This series will hopefully coincide with breakthrough in the progress sense. As noted above, it’s relevant to Free software advocacy because what we have here is a former FSF sponsor basically robbing (defrauding) Free software advocates, who were exploited and subjected to “value extraction” for many years, grossly underpaid and moreover embezzled behind their backs with a pension that never existed.

We’ll hopefully be able to illuminate what’s happening behind the scenes by disclosure of some redacted communications.

Retrieval statistics: 21 queries taking a total of 0.108 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|