Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Archive for the ‘Security’ Category

Matthew J Garrett Put secure-boot and shim in Linux and It’s Breaking Systems Again

Crossposted from Techrights

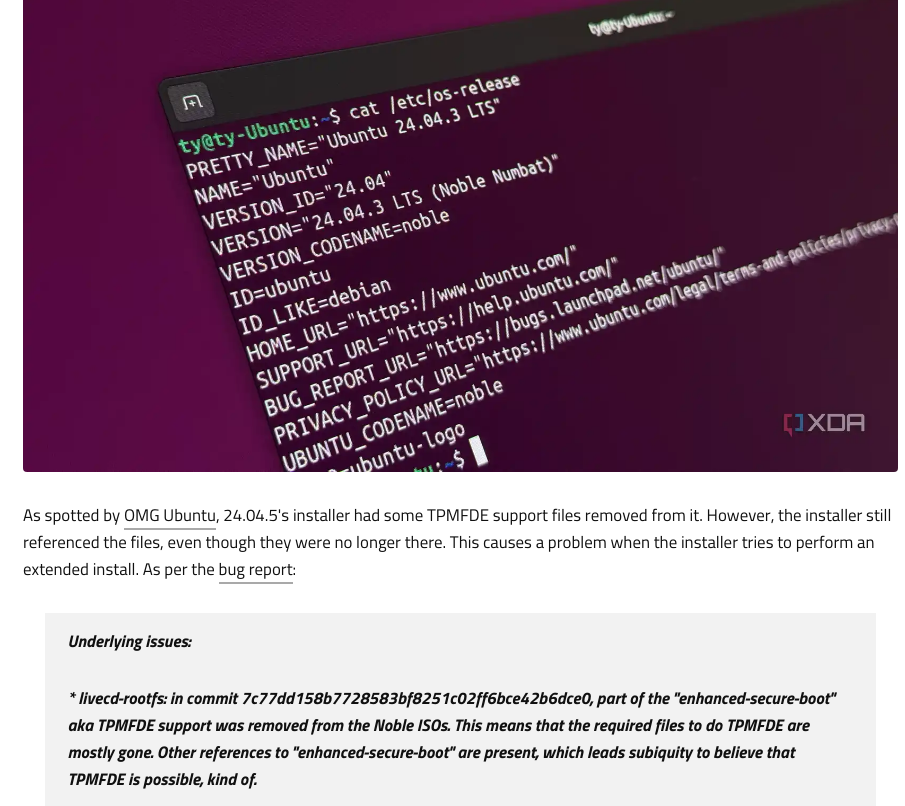
Fake security is already breaking systems running GNU/Linux

Ubuntu secure boot

More complexity means more problems. Newer code means more bugs (e.g. Rust rewrites).

Fake security means catastrophe for no actual gain/s.

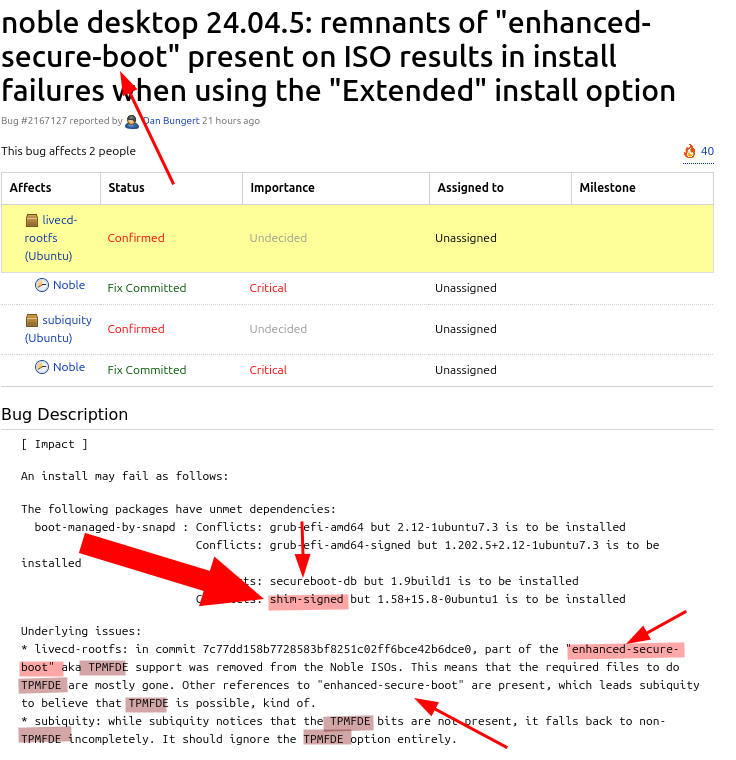
As noted by several sites [1, 2], linking to a bug report, kneeling to Microsoft came at a high cost:

enhanced-secure-boot

TPM? Who asked for TPM in Linux? GAFAM? But who am I to even mention the principal culprits? I have degrees in computing, not in genetics.

Near the Action at the Stadium

A perk of living next to major facilities of non-military nature (datacentres [1, 2] are used for military)
Arrivals....

I think I neglected to mention a sort of “uptime privilege” this morning. I realised this only later. It’s a kind of an “RK” privilege one can forget about. You take this for granted when you’re next to international games or actions.

My computers have high uptime records owing to good electricity infrastructure (reliability/uptime/availability); we have a sort of fortune or the mere luck of having very reliable electric grid (near a very large and famous stadium) with persistent connections and decent hardware nearby, fallbacks included, with no natural disasters, not even floods (we’re in a slope).

In some parts of the world they have extreme weather this year, including prohibitive costs of living (UK minimum wage a lot higher than the average in Europe), war, conscription, and worse. Here, unlike Ukraine, no shelter time (or risk of being hit by missiles), is expected, so carrying on as usual is almost always possible. Until someone from another continent pays $130,000 to drag you down to London. But even then, your computers remain turned on at home.

Manchester Airport Data Breach

The data can be used to defraud (e.g. impersonate) people who flew to and from Manchester Airport. Worse yet, it can potentially be leveraged for blackmail.

Groups of tourists have gathered for the holiday around here, maybe anticipating the start of the football season. They’re typically quiet and polite people from Europe or east Asia. They choose to come to Manchester, not London, or sometimes both. They shop, stay overnight, and eventually leave to go back home.
Recently there was a data breach in Manchester Airport. Airports keep a lot of personal information about the people who fly and fliers cannot opt out because nobody can board a plane anonymously.

I certainly hope the computer systems at Manchester Airport were properly partitioned and did not use Windows. Every version of Windows has back doors and is a ransomware magnet.

“DDoS” is a Very Broad Term

To each its own

Getting a solution to DDoS attacks is not easy because each time the pattern to tackle (without false positives) is a bit different and each incident can be unprecedented in one single site, so there’s no one-size-fits-all solution.

At the moment we combat another wave of nuisance bots and each time it comes there’s risk that everyone will be “away from keyboard” and therefore it won’t be detected.

Cyber Attacks and More

Wormwood Meteor Of Revelation

There are cyber attacks against our Web sites this week. These attacks take several different forms. These are clearly censorship attempts. We have paper trail to prove that.
Any attacks – no matter their form – tend to indicate fear. In this case, the fear is that information that we published will be available and remain available for many years to come.

Sustaining attacks is one thing; reporting them is another. What’s happening is illegal. It will be treated as such.

We’ll carry on publishing as usual. Curtailing access to information is never a winning strategy for all sorts of reasons.

DDoS Attacks: Tux Machines and Techrights Impacted

I AM not sure who is doing this and why, but the server of Tux Machines is under DDoS attack. It impacts Techrights as well. I wrote about this back in April when it began, then again ~3 weeks later.

The Web is so chaotic on so many levels.

CDNs are not the solution. Access gatekeeping with JS is not the solution either, it’s another new problem.

You Can Hate Donald Trump and Object to Electronic Voting Machines at the Same Time

Schismogenesis in Bill Gated-funded sites (those machines run Windows with back doors):

Schismogenesis

I NEED to clarify upfront I do not believe the 2020 election in the United States was “stolen” and I do not support Donald Trump. He disgusts me.

The United States is still “using fraudulent voting machines” with back doors, a friend has reminded me. But the media giants aren’t talking about and “associating opposition to fraudulent voting technologies/products with crazies. Other crazies will defend fraudulent voting technologies/products for no other reason than those two crazies are opposed to them…”

Techrights did at least 2 “statements” on this issue [1, 2] just to clarify voting machines are no good regardless of news sites’ rhetoric.

Quit using opaque electronic voting machines and then lessen the likilohood of armed fanatics storming government buildings in an act of overt insurrection.

Retrieval statistics: 21 queries taking a total of 0.093 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|