Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Archive for the ‘Personal’ Category

Microsoft Skype is Not Open Source

Video download link | md5sum 9088e5ce7cc9eba79bde5977c20d399f
Sirius and Microsofters Inside
Creative Commons Attribution-No Derivative Works 4.0

Summary: Sirius ‘Open Source’ has been employing incompetent managers for years — a sentiment shared among colleagues by the way; today we examine some glaring examples with redacted communications to prove it

LAST night we published this latest/next part about Sirius, though only about a day later than originally expected due to my most important hard drive simply dying. We’ll still try to stick to the original schedule with a closing day after exactly 2 months (since the start of the series). After that we have more to cover, but maybe not on a daily basis.

The video above goes back to the days when a backstabbing manager had been appointed; he asked if not demanded all of us to get Microsoft Skype accounts and get the darn thing installed only for useless presentation based on invalid data.

The video moreover gives a recent example of “managers” failing to do very simple and very critical tasks. This puts clients’ businesses at great risk.

Sirius hasn’t been managed by competent people for years already. Clients are noticing this, but some chose Sirius because of very old past reputation (and revisionist history).

The Time Sirius ‘Open Source’ Forced Staff to Install Microsoft Skype on Personal Devices

The time a Sirius manager demanded that all staff installs Microsoft Skype, creating an account in it

“I found what they call a whitepaper but it’s 17 pages and basically says “We’re ISO certified”…”

–Mathew Duggan, blog post from yesterday

Summary: Sirius ‘Open Source’ was hiring people who brought to the company a culture of redundant tasks and unwanted, even hostile technology; today we continue to tell the story of a company run by the CEO whose friends and acquaintances did severe damage

YESTERDAY I had a major hardware incident (the hard drive of my main PC suddenly died and needed replacing), so there was no article about Sirius, but today we’re catching up fast (I’ve also upgraded the operating system).

Looking back at my time at Sirius (it’ll be 12 years in 2 weeks from now), I try to recall the better days, the early days. These times weren’t fantastic by any stretch of imagination, but they were certainly better. Free software was used at every level. The colleagues were looking after the physical infrastructure. The NOC colleagues adopted my handover format/style over a decade ago and management had better temper.

More recent managers didn’t understand Free software or “Open Source”. One of them fell in love with Microsoft’s proprietary junk, even several years before Gates Foundation money (Gates Foundation paid under some NDA, resulting in the formation of Sirius Open Source Inc.). He said in Twitter that “some things” are better entrusted to Microsoft and, as it turned out later, he allegedly worked against the company (the CEO said he was trying to liaise with one of our colleagues to “steal” our biggest client).

By contrast, his predecessors were very much involved in GNU/Linux. One of them is mentioned in an old talk: “The LiMo Foundation are building a mobile middleware stack based on Linux. With over 70% of the platform based on open source components, what are the benefits and challenges of open source adoption, and what is the LiMo approach to working with Open Source?”

We also had highly technical managers before that; of course they use GNU/Linux. At the moment it’s safe to say that nobody, at least among the managers, uses it. The non-technical Office Manager probably uses a “phone” some of the time (instead of a “proper” computer) and probably has no clue about any of the technical details or the tasks inside the company. A ‘box-ticking’ ‘bullshit job’ is the only thing coming from her direction and she’s failing even at that, repeatedly, then vanishing without replies/explanations (or just some lousy excuses).

Below we present some redacted evidence of the issue spoken about above. Here’s the handling of “Failed PSU”. As per Handover to Shift 3, 22/07/19: “Renewed the warranty for xxxxx. Don’t tell the customer that it ran out. (xxxxx’s email address was the one listed. I’ve changed that to the support email/number.) Checking that it is plugged in before xxxxx calls in the warranty.”

So the very simple task of renewing the warranty was not done. Handover to Shift 1 10/08/2019 said: “Both xxxxx and I have attempted to claim the warranty on this, but the HP Carepack Centre say they will not send out a new power supply without seeing the logs. The warranty did not cover the time that the logs will show that the PSU failed, so unless someone can figure out a solution then we are stuck. Whilst this server only has one working PSU it is at risk, so we need an idea.”

Notice they keep the customer in the dark about this. Handover to shift 3 – 24/08/2019: “xxxx received the xxxxx and said he was fitting it on the 19th. Waiting for update when he returns from holiday on 4th September.” More recently a similar incident, as per Handover to shift 1 – 11/09/2022: “Looked for the warranty certificate. (She hasn’t sent it to support, so checked my own emails and slack too.) xxxxx said she would send it out before she went on maternity leave.”

So one can see what it means to have irresponsible ‘box tickers’. Clients’ server are at risk of physical damage.

Regarding the above-mentioned Skype episode, another ‘box ticker’ prepared a useless presentation based on bogus data and wanted all the staff to install Skype, even though it was proprietary and already controlled by Microsoft.

This is him:

Skype accounts

Dear All

Very soon we will be holding an Operations Staff Skype call to deal with activities, processes and customer service ethos of the team. If you need to create a Skype account, please do so by Tuesday 24th March. A camera is optional, but you will need a microphone.

Once you have a Skype account, please add me as a contact: xxxxxxxxx. I will need this information to join you to the call.

Kind regards

xxxxxxxxx

My reply:

Hi xxxxxxxxx,

Will it be possible to connect through landline/mobile/NOC phone (Cisco) or SIP? Also, what date/time is the event? It looks like it says 27/3 (Friday).

Thanks,

Roy

His:

Hi Roy

The event is Friday 27th March at 10 am. I shall be using slides on the call, hence my request a few days ago that everyone connect to my Skype account.

Regards

xxxx

After a lot of pressure I found some old (very old) Android phone from 2012 and temporarily put Skype on it.

I need to find some machine that I can afford to compromise (maybe a phone). There are passwords and stuff on this machine, so installing Skype on it is out of the question (too dangerous).

He thanked me, ran a totally useless presentation on this, and then I deleted the whole thing.

This is what he wrote to all the colleagues, promoting Microsoft’s Skype to them:

I note there are a number of team members that have not yet added me on Skype. Please do this in preparation for Friday’s meeting.

Regards

Also:

Dear All

Here’s a check list of what you’ll need to do to prepare for tomorrow’s call and some guidance for joining the call.

1. A Skype account
2. Be connected to me. Skype name: xxxxxxx
3. Audio: mic and sound. We probably won’t use individual video links as this can cause bandwidth issues
4. Reasonable screen real estate so that you’re able to view some slides
5. A quiet space — background noise will be distracting to others on the call

Notes:
1. It’s best to mute if you’re not speaking
2. At 09:55, open a Skype session. I will add you to the the call. Once everyone is added I will host the session by initiating the call
3. Folks in the office may find it easier to gather around 1 or 2 machines
4. If you haven’t connected to me you cannot be joined to the call. If you’re not on the call you will miss important information

Regards

Not so long later he left the company after (according to the CEO) it turned out he had been working against the company behind the scenes.

Dear All

It’s time to say goodbye and I wanted to say thank you to each and everyone of you for my gifts, cards and especially, for my “bag for life!” Very topical!

I have enjoyed my time at Sirius very much — you are an inspiring bunch to work with. And for sure, you collectively pack-a-punch that puts Sirius fairly and squarely amongst far larger competitors. I may no longer be inside the tent, but please be assured, I will remain a Sirius fan.

Farewell Sirians

All the best

xxxxxxxx

That said nothing about the real reason he left.

So that’s another story for these chronicles. In the next couple of days we’ll show some more stories and then conclude/summarise the series.

Sirius Outsourced to Google and Everything Broke

Video download link | md5sum 74987f7fa344dfdc3ef4a4d40f5045ef

Hell, Sirius, Anybody There?
Creative Commons Attribution-No Derivative Works 4.0

Summary: In my final year at Sirius ‘Open Source’ communication systems had already become chaotic; there were too many dysfunctional tools, a lack of instructions, a lack of coordination and the proposed ‘solution’ (this past October) was just more complexity and red tape

“HELLO, anybody there?”

Hell no. Wait till we authorise the microphone, open the correct browser window, and then roll up some scripts. Within 3 rings! Yeah, right! No way! On old hardware that can barely cope with epic bloatware imposed on all staff by the stingy management.

Sirius never provided us with hardware (other than a very old and second-hand Cisco phone), but it expected us to multi-task with a whole bunch of junk and up to three telephone systems running in parallel. Does that sound like a competent company? Who made these decisions? And who’s being blamed? Decision makers? Proprietary software? Or the victims of both?

The video above explains the absurdity of the telephone system at Sirius, which was only getting worse over time because incompetent people were calling the shots behind closed doors and without consulting those affected by their decisions. Not to mention how they repelled or scared away Asterisk-capable engineers. As it turns out, technical people were starting to have technical issues with the new “Google” system, which they could only object to after it had been pushed down their throats.

The moral of the story is, don’t outsource communications to proprietary software, do not rely on clown computing, and don’t let incompetent people make decisions (more so in the dark, in secrecy). It would harm both staff and clients and at the end the culprits will refuse to take the blame, instead insisting that they can salvage the whole mess by going deeper into the trap which caused the mess in the first place.

Sirius is broken beyond redemption because it is now governed by truly incapable people, shielded by a culture of intimidation and surrounded by sex partners who blindly follow orders/instructions.

And those are just the technical aspects, not the legal ones.

“The ISO Delusion” (latest part) explained privacy or data protection aspects; ISO certification doesn’t mean compliance with common sense like companies controlling their own communications and protecting clients’ sensitive data, including passwords and private keys.

Sirius ‘Open Source’ Sabotaged From Within

Video download link | md5sum 3fa713aa016effddd846715afa98523f
Sirius Abandoned Everything
Creative Commons Attribution-No Derivative Works 4.0

Summary: Staff with technical skills won’t stick around in companies that reject technical arguments and moreover move to proprietary software in a company that brands itself “Open Source”

DESPITE losing my best friend this week I am trying to keep active and to keep this series going. My friend helped inspire my activism and many other things. The video above explains some of the things that happened at work, based on practical examples (demonstrating that ISO certification changed nothing for the better). More people need to find the courage to confront their bosses and demand justice. Don’t just “play it safe”, try to actually fix things, from within if possible (taking this public is the very last resort).

The video above contains some of the backdrop to the collapse of Sirius ‘Open Source’. It comments on this post. The Gates Foundation was never mentioned in writing at Sirius, only once and strictly verbally in 2019. An NDA signed by Sirius Open Source (yes, that’s an actual sellout considering what the CEO used to believe in*) changed things for the worse and resulted in the CEO being ‘in exile’. We’re talking about a fervent Microsoft critic, who [cref 168438 moved the company to Washington] for the “first US client” (yes, Gates) and weeks after it all happened not only myself but also my wife got falsely accused. We were acquitted only after months of humiliation. Nobody ever apologised for this.

Back then, as well as in 2017, I wanted to publish “Microsofters Contact My Employer to Get Both My Wife and I Sacked” (yes, it happened prior to 2019 as well). It’s truly quite maddening what Microsoft and its goons would do to silence me; they even pick on loved ones. This became a potential future topic way back in 2016.

More recently after I told a friend that Bill Gates, not Microsoft, was paying Sirius Open Source Inc. (with the actual timing being interesting; coincidence being improbable) a manager intentionally twisted/distorted what I said. What I said was factual, what they said I had said was not. Gates never needed British company to handle something thousands or American firms can easily handle (let alone ask this company to establish itself in another country, which is possibly what happened though the NDA hides it).
___
* Here’s one old talk that covered “FUD (‘Fear, Uncertainty, Doubt’) as the nonsense that it is [...]”

International Organization for Standardization (ISO) Certification Does Not Assure Anything

The International Organization for Standardization (ISO) certification process means almost nothing. It’s just a glorified brand. Deep inside many people and organisations know it.

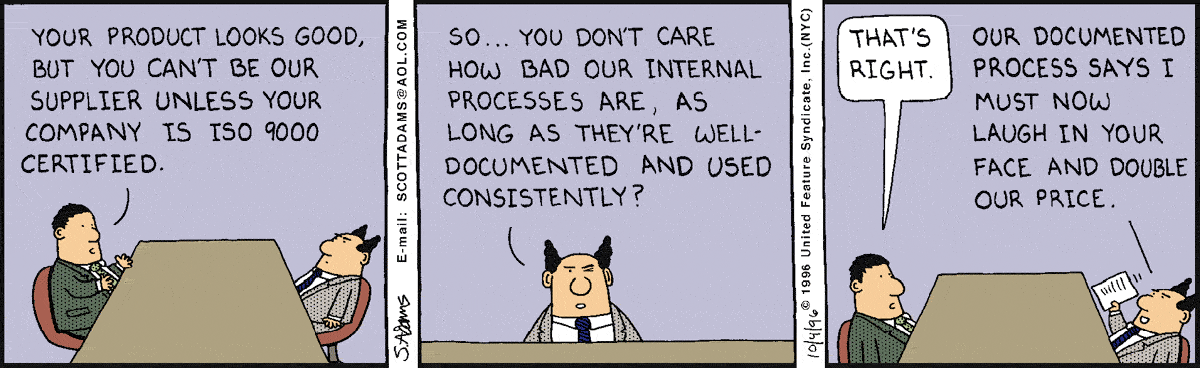
Dilbert on ISO
Dilbert on ISO 9000 Certification in 1996 (there are also 21 for ISO 9001)

Summary: Sirius ‘Open Source’ was good at gloating about “ISO” as in ISO certification (see our ISO wiki to understand what ISO truly is; ISO certification needs to be more widely condemned and exposed) while signing all sorts of dodgy deals and lying to clients (some, like the Gates Foundation, were never mentioned because of a mysterious NDA); security and privacy were systematically neglected and some qualified as criminal negligence (with fines/penalties likely an applicable liability if caught/reported)

THE past few days were spent explaining ISO certification in relation to Sirius. The next few days will be spent giving an example or a sub-set of examples of how Sirius handled sensitive data. It probably hasn’t improved at all since I left last month.

For some essential background, Sirius Open Source Inc. (not SIRIUS CORPORATION LIMITED) was grabbing Gates Foundation money back in 2019 — all this while registering in the US for this “first US client”, letting Windows users who adore surveillance get involved in decision-making while outsourcing more and more of what’s left of the company to dubious companies with NSA connections.

The problem here is that Sirius had British clients with their clients’ data on the systems. Some was medical data. What does the law say about access from another country and why was Google (American company) getting/drowning in legal hot waters for involvement in the NHS?

What’s more, it’s not clear if ISO 9001 certifiation allows personal computers at home, purchased and maintained by staff along with many other uses and applications, to be used as work machines (deemed “Secure”? Really???). Remember that, as we noted repeatedly in the past, the managers never bothered supplying the staff with anything; the company does not even provide a chair and a desk, as already explained in length here (mostly back in December). Did that pass muster at ISO’s cash register (ISO just wants the money)?

Well, maybe in the ISO forms the company can pretend that those computers were supplied by the company to staff when in fact the staff receives almost nothing from the company except a very old phone (Cisco-branded, Ethernet only; maybe 2 decades old).

While I’m not going to report this as a former insider, I do wish to explain what’s at stake here, at least as a cautionary tale. ISO doesn’t care; it has no quality control of its own; its workers are like corporate staff and they might not even care anyway; they got the money, and that’s what’s important to ISO. Many questions remain, e.g. which actual shell was the certification for? Do they realise they deal with a hydra or a polymorphous entity here (some of its shells are based in another continent, without actual boundaries within the company)? Even the pension schemes seem to be struggling to keep track and they need to be lectured on how the company splits and then illegally compels staff to sign papers without legal advice (nor proper understanding), as we noted here before. It was covered a lot roughly one week ago.

And sure, many lessons are to be learned outside the company, too. If regulators could find E-mails, they would not struggle to see incriminating stuff (we plan to add examples to the wiki), including NHS medical data “oopsies” (admission on the record, too), even for people do not consent to data sharing. ISO probably doesn’t care. As we said several times already, ISO only cares about money. With ‘anonymisation’ not working, accidents aside, there’s a big scandal brewing under the surface, but then again the privatisation of the NHS would likely misplace the blame. The media has several examples of known incidents and it’s a very big deal because the NHS has been pushing towards it, moreover offering to send some of this data abroad.

To be clear, NHS was not a client, except indirectly (contractors). But if someone wishes to find some major scandal/blunder, we welcome further investigation, i.e. people can do what ISO ‘cannot’ do because it would discredit ISO.

“There are 2 problems to track,” an associate noted, “one is the scam of the ISO 9000 certification. The other is the destruction of ISO as an organisation by Microsoft.”

International Organization for Standardization is an Elaborate Scam

Video download link | md5sum cc29a588d814b375a666bda5d567b58f
What Sirius Teaches Us About ISO
Creative Commons Attribution-No Derivative Works 4.0

Summary: Based on my experiences inside Sirius ‘Open Source’ — as I was there for nearly 12 years — I finally tell what I’ve witnessed about ISO certification processes (see ISO wiki for prior experiences)

Sirius ‘Open Source’ taught me a whole bunch of things; some were valuable technical skills, but many were negative experiences that I can finally explain out in the open, expressing in words various ideas that I formed (or formulated) years ago.

The above video concerns ISO and it is relatively long because it covers two parts instead of just one, starting with background and proceeding to real-life examples in the form of redacted E-mails.

The conclusion I reached years ago is that ISO is somewhat of a scam. It creates a barrier that mostly protects monopoly and it makes a lot of money by giving worthless papers, essentially turning managerial ‘religion’ into a fat cash cow. If more people understood the business model of ISO, maybe there would be no ISO anymore.

How to Buy ISO Certification (It’s Easy!)

International Organization for Standardization (ISO) brag

Summary: Before we proceed to showing how Sirius ‘Open Source’ blatantly ignored security and privacy we wish to show how ISO (see ISO wiki) basically ‘sold’ a certificate to Sirius — this is like a “diploma mill” but something that’s for businesses, not individuals

THIS is today’s second article on this topic. We’ve found some spare time for faster progression and in-depth coverage. As I noted yesterday, my wife had more direct and indirect experience (decades ago) with ISO being a bunch of meaningless hooey. So did I (having stumbled upon classical ‘box tickers’ or worse). Sirius is just another reminder of that. Hence this series and its relevance. It seems like a lot of people in technical fields separately and independently reached the conclusion that ISO is overhyped, overvalued, and mostly a waste of time and money (unless you have a ‘bullshit job’ to justify).

“This isn’t science. It’s like calling “economics” a science. It is not. It’s more like religion.”“My dad complained about the ISO in the 90s,” Ryan said in IRC an hour or so ago. “He constantly made fun of all of their “standards” for management of a company that didn’t mean anything but go on and on. It’s a sort of code so that managers sound smarter than they are. “We’re ISO-Whatever compliant with our handling of the TPS reports.” And the ISO standards can be wrong and never revised. Microsoft implemented the standard for MP3 and so did LAME, and then the result was they were both correct and Windows XP crashed. Part of the standard about what constituted the maximum size for a frame could be calculated one of two ways.Microsoft chose the more constrained way and it resulted in a buffer overflow with some files that crashed Windows Media Player. LAME had chosen the method that resulted in a slightly larger permissible frame size. The outcome was LAME had to be changed to use the Microsoft calculation to avoid crashing Windows, and that meant a reduction in audio quality under some circumstances, with padded bytes instead of data. Later, they changed to use the VBR bit allocator, even in a CBR file, and it mostly avoids the situation by its method of action. It can cleverly use the bit reservoir in ways that the former bit allocator that was only for CBR files couldn’t. Naturally, they never delete anything, so you can still demand the old model. It’s just an absolute nightmare of options switches. It’s the worst thing I’ve ever seen in a utility its size. ISO is kind of the stuff of Pointy Haired Bosses when it comes to Management Theory being standardized.”

Well, this whole “Management Theory” is what we’re dealing with here.

This isn’t science. It’s like calling “economics” a science. It is not. It’s more like religion.

Here’s what happened in Sirius (in mostly logical/chronological order):

Subject: ISO
Date: Mon, 29 Jul 2019 15:47:43 +0100
From: xxxx
To: xxxx

Hey All,

As you know we are going through the ISO processes – I have been asked to gather some information from everyone at Sirius to create a list of all assets used by employees of Sirius whether it belong to the company or the employee so if I can have the item name and serial number that would be great. They have also asked which anti virus you all use.

Are you all able to send me the required information ASAP please?

Thanks,

xxxx

Yes, because a bunch of serial numbers would mean so much! Of people devices at home… for the most part.

“They would nag us to do the same ‘course’ every year, even though it is dumb and we ‘passed’ it already.”A month later came “You have been registered for a Training course – Information Security” (no, not really security but this hoax instead). We’ll deal with that another day…

They would nag us to do the same ‘course’ every year, even though it is dumb and we ‘passed’ it already. This is compliance???

??”This is something that will be done annually for our ISO process,” I was told, “so please complete this on your next shift.”

??Way to waste people’s time, doing and passing a total hoax over and over again (details on why it’s a hoax were covered here before).

??Notice the threats being sent to ALL staff:

Hi All,

As you will all be aware we have been implementing new policies and procedures in order to become ISO 9001 and ISO 27001 compliant. Part of this entailed changing our HR company to xxxx who use the online portal Atlas to provide an easier method to roll out training. I have checked and there is still a substantial amount that has still not been completed.

ALL training sent out by myself needs to be passed and completed by the _*25th November 2019*_. This is to ensure we meet our deadline for the final stage of ISO audits.

Failure to comply with this request may result in disciplinary action. For those of you that have completed the training, please ignore this message and thank you.

Kind Regards,

xxxx

“Failure to comply with this request may result in disciplinary action,” it says. They kept making veiled and explicit threats. Sometimes this culminated in actual bullying, false accusations, and blame-shifting witch-hunts.

Of course the portals failed to even work properly. For instance:

> ALL training sent out by myself needs to be passed and completed by the
> _*25th November 2019*_. This is to ensure we meet our deadline for the
> final stage of ISO audits.

I was able to open all the documents and read them. The animated things,
or training sessions, get stuck. I tried each one of them about 5 times
(>each<) and they get stuck somewhere along the way. I tried this on
multiple machines. Rianne told she too had some difficulties.

I will try again on my next shift, but these technical issues do merit a
mention. They also rely on plugins Adobe no longer supports, posing
security risk (an issue aside from the bugs).

Kind regards,

[Roy]

Her answer was: “Have you tried using a different web browser?”

Of course she wasn’t using GNU/Linux or anything “Open Source”. This does not constitute an actual solution.

In 2020 the following was sent:

——– Forwarded Message ——–
Subject: xxxx – Things to do
Date: Thu, 26 Nov 2020 11:38:01 +0000
From: xxxx
To: xxxx
CC: xxxx

Hi All,

In October I issued Linux Training via xxxx. Can you all please ‘acknowledge’ this on your portal to show that you have opened and read it.

I also need you to ensure ALL training modules issued on xxxx i.e information security and documents issued i.e IMS Awareness presentation have been completed by the end of your next shift.

It is essential these tasks are carried out prior to our ISO Audit next week.

Kind Regards,

Well, those training modules and ISO guidelines weren’t even followed by Sirius. We gave examples of this before. In some cases, there were efforts to meet standards only after a certificate had been granted.

Sheesh. I’m not supposed to say this in public, am I?

What did those audits mean anyway? What did the above “ISO Audit” actually check? That the cookie drawer is properly locked when Office staff goes to retrieve some hot chocolate milk from the machine?

“In the next few parts we’ll show what Sirius did in practice, not in theory, and what it told staff, not ISO auditors.”Some other messages were banal. They indicated a certificate had been granted (in other words, Sirius basically bought one) after minimal so-called ‘audits’ and staff sending a bunch of numbers from the back of computers (as if that means anything at all).

ISO is a joke. When it comes to this administrivia, ISO created just another ‘cash cow’ for itself.

In the next few parts we’ll show what Sirius did in practice, not in theory, and what it told staff, not ISO auditors. It’s one heck of a clusterf**k with the company’s data scattered all over the place. That includes clients’ data, even private keys and passwords.

Retrieval statistics: 21 queries taking a total of 0.125 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|