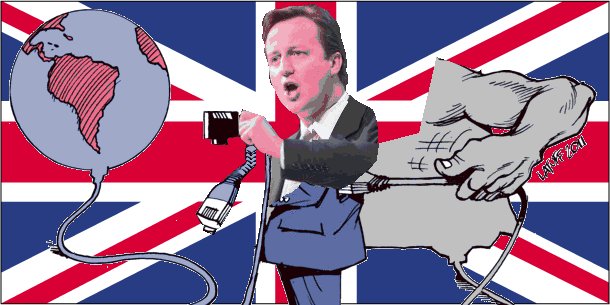
Privacy in E-mail Nearly Impossible
 Filed under:

 lmost one decade ago I shifted all of my E-mail to a domain that I control. Well, to be accurate, my host and I control it, and that host is based in Ireland/UK. But over time it became apparent that this was usually useless for privacy. If the recipient uses an E-mail address in one of the big providers of ‘free’ E-mail services (e.g. Yahoo, Google, Microsoft), then my messages (incoming, outgoing) will be visible to corporations and governments whose business should not be other people’s personal lives. So among those who were close to me I was pushing to move to a private domain as well, often the same as mine. This goes back to around 2004. Alas, this wasn’t enough. People routinely use SMTP servers provided by their ISP (‘free’ traffic, free to engage in surveillance), and some use Web-based clients that spying-happy browsers are accessing. Those browsers got worse in that regard over time. Ubuntu now uses search to turn users into products. Besides all of this, the ISP has access to packets, and here in the UK we have Phorm, which helps ISPs do DPI (deep packet inspection) under the guise of “marketing” surveillance.
The bottom line is, encryption for E-mail is needed, but the problem is that few mail clients actually support PGP. Some make it cumbersome to use. Perhaps it’s fair to say that privacy in E-mail is almost an impossibility in practice (even among two willing parries). I no longer use E-mail all that much. face-to-face conversations remain one of the most private options for those who value privacy.


 or many years I had abstained from joining Reddit, which I subconsciously viewed as a competitor to Digg, where I was already quite prominent and sometimes called “omnipresent”. But several months ago I reconciled all this nonsense and joined the site — a site that I


 ROBABLY stating the obvious here: the Internet was created to endure targeted attacks and the World Wide Web was created by a British lad who wanted to share his physics papers. Nowadays, the Internet and especially the Web are challenging the old conglomerates because they offer low-cost competition. Those with trillions in the bank account (aggregated wealth) are not going to give up without a fight; using their bought politicians they are not trying to manufacture new laws, such as ACTA, which
 INYURL used to be one among few services that shortened long URLs for people (snipurl was another). These services would typically be used only when a URL was exceptionally (and perhaps irregularly) long — to the point of being incompatible with some mail/news readers. The landscape has changed somewhat and nowadays, with people becoming lazy and phone-tied, folks assume that original URLs don’t matter, even though they indicate their source, their date, and perhaps title as well, at least most of the time (if properly designed at CMS level). URLs are not merely barcodes, their visibility contributes a lot toward expectation and even the ability to recover broken URLs in the future (based on their source or title). Now that every John and Jane creates his or her own shortener, there is less incentive to keep those services up in the long run, especially once they drive a lot of ‘legacy’ traffic and do nothing for revenue (mere redirections). As the creator of the World Wide Web put it about a year ago, there is also the danger that authorities of TLDs will sooner or later be misusing their power to censor some popular shorteners and immediately break a whole lot of linkage, upon which much of the Web is based. In a sense, short URLs break the Web, but when there are limitations on the number of characters in services like Twitter, people are pressured to use them, even by default.