Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Monday, July 24th, 2023, 1:17 am

Deaths Soared 17% for Young Adults in Just Four Years

UK deaths H1 2023: Deaths by week, by age range/bracket; Totals shown

IF the pandemic is over and we can give up on distancing and masking, then how come so many more people die (than before the pandemic)? For my age group (ages 15-44) in England and Wales, 7,455 deaths were registered in 2019 H1 (January-June), compred to 8,709 deaths in 2023 H1. That’s a 17% increase in deaths in just 4 years.

How come?

The deaths of under ones in 2019 H1: 1252. 2023 H1: 1281. For ages 1-14 it’s 512 deaths in 2019 H1, 505 deaths in 2023 H1. So they did not really suffer as much. It’s widely known that COVID-19 has little effect on young people. here are the complete numbers.

Age under 1: 1281
01-04: 197
05-09: 116
10-14: 192
15-19: 484
20-24: 644
25-29: 901
30-34: 1455
35-39: 2187
40-44: 3038

Wednesday, July 19th, 2023, 5:32 am

Forms for Reporting Data Breaches Exist to be Used and for Those Affected to Get Notified

Summary: One last note on the issue of Greater London Authority (London Municipality); even though forms exist to report security breaches or incidents of data breaches, Greater London Authority never seems to have bothered with this; the culmination of this in the media (a scandal which puts at risk victims of sex crimes) overlooks a history of repeat/recurring incidents

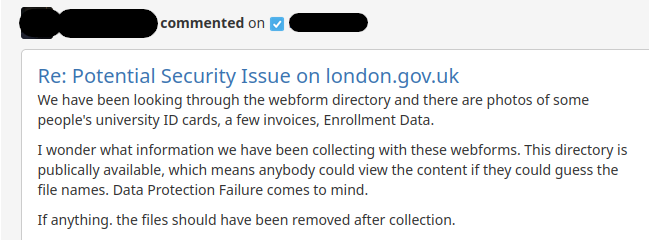
As far as I’m aware, this was never reported (to those impacted) except internally.

GLA staff (it wasn’t the first such issue, nor the last):

GLA: Drupal access

So what good are such forms?

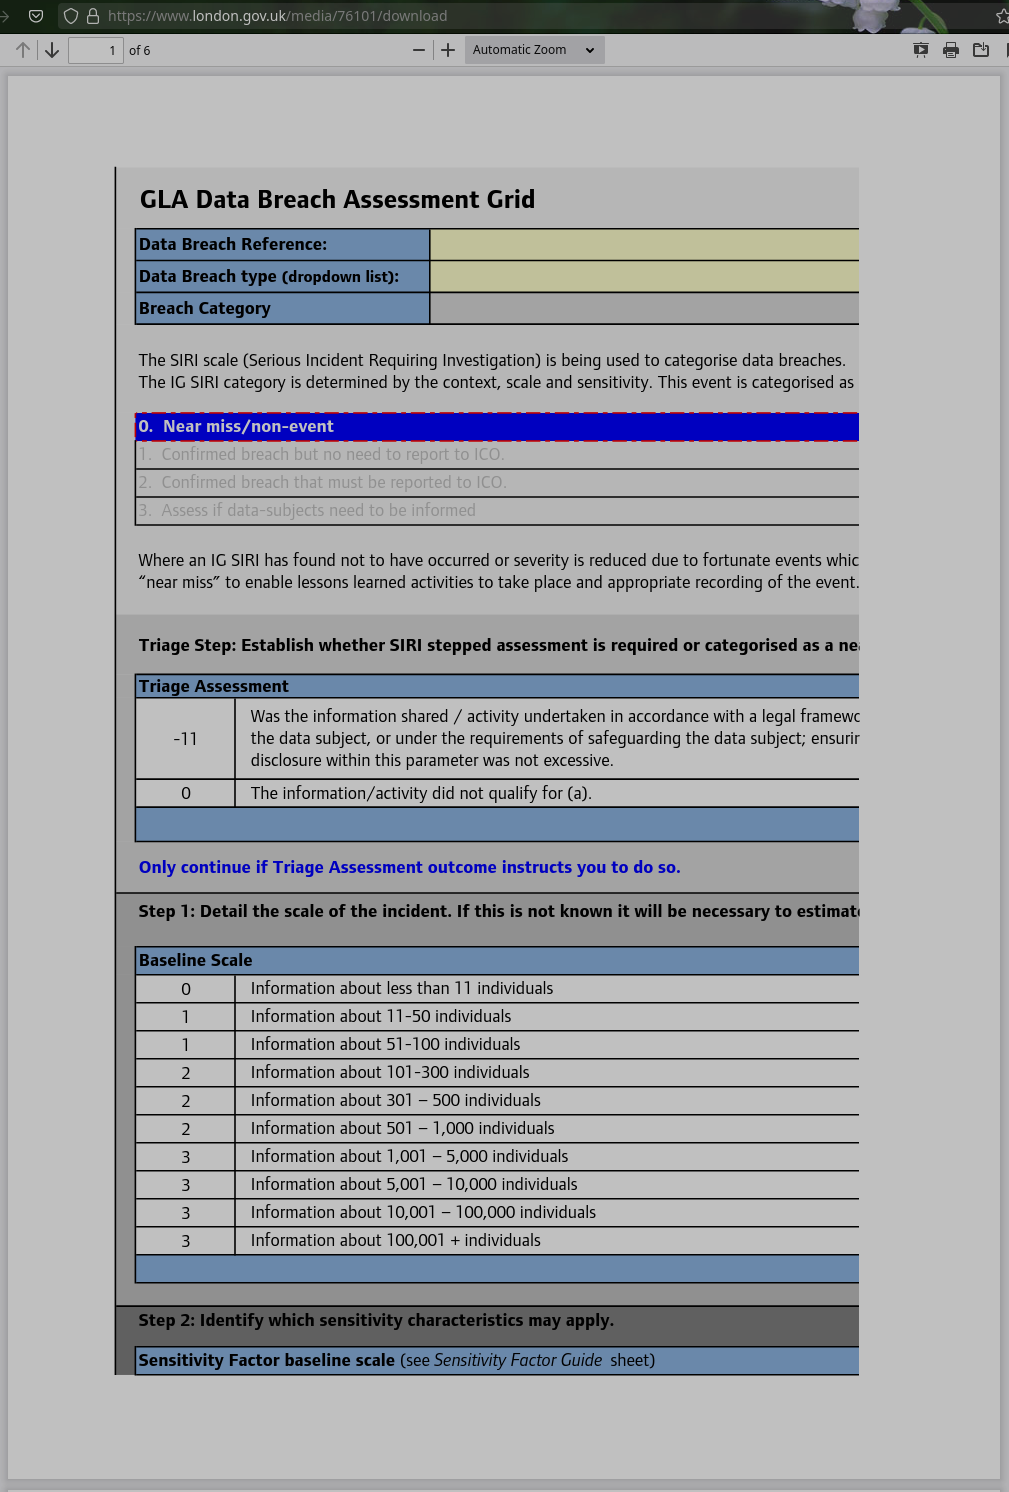
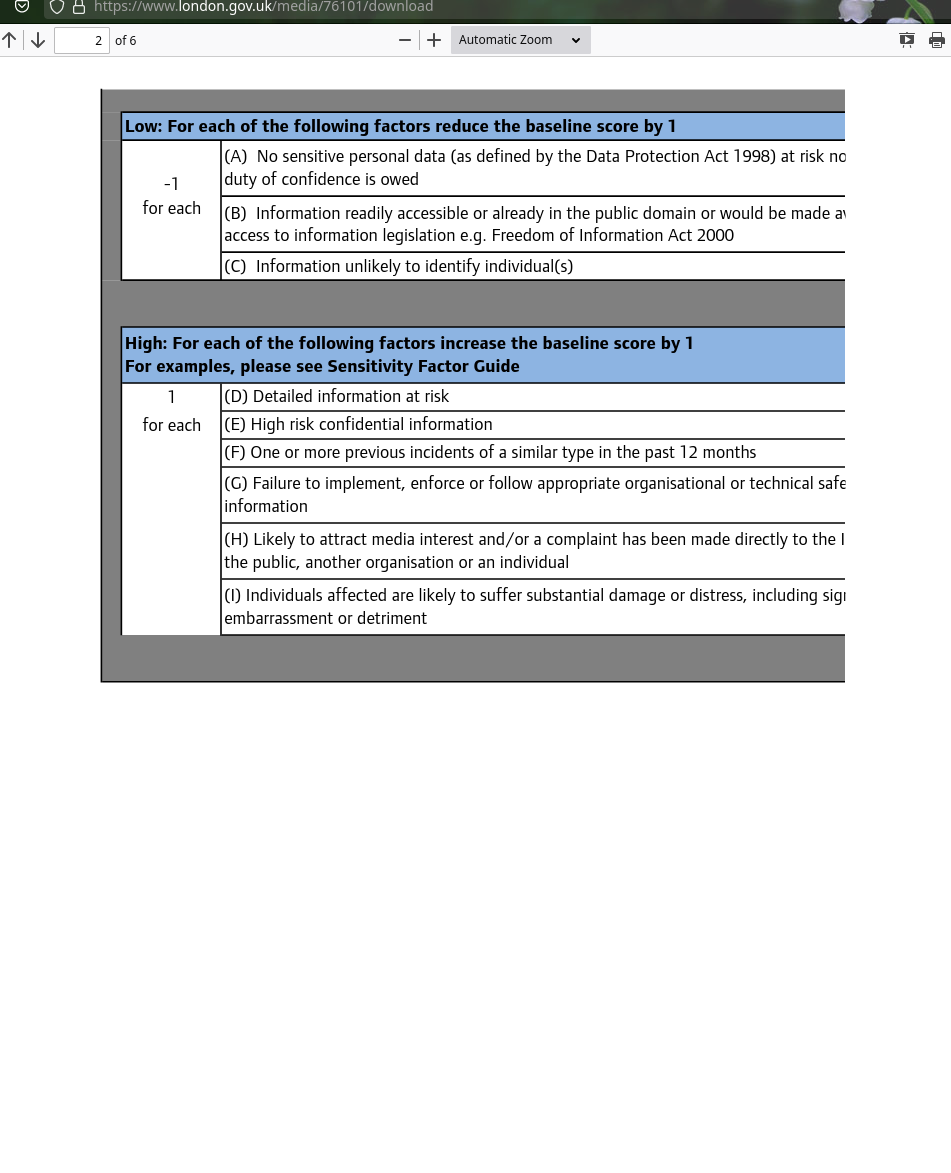
GLA form for data breach #1

GLA form for data breach #2

Monday, July 17th, 2023, 11:44 am

Greater London Authority Fails to Meet GDPR Rules

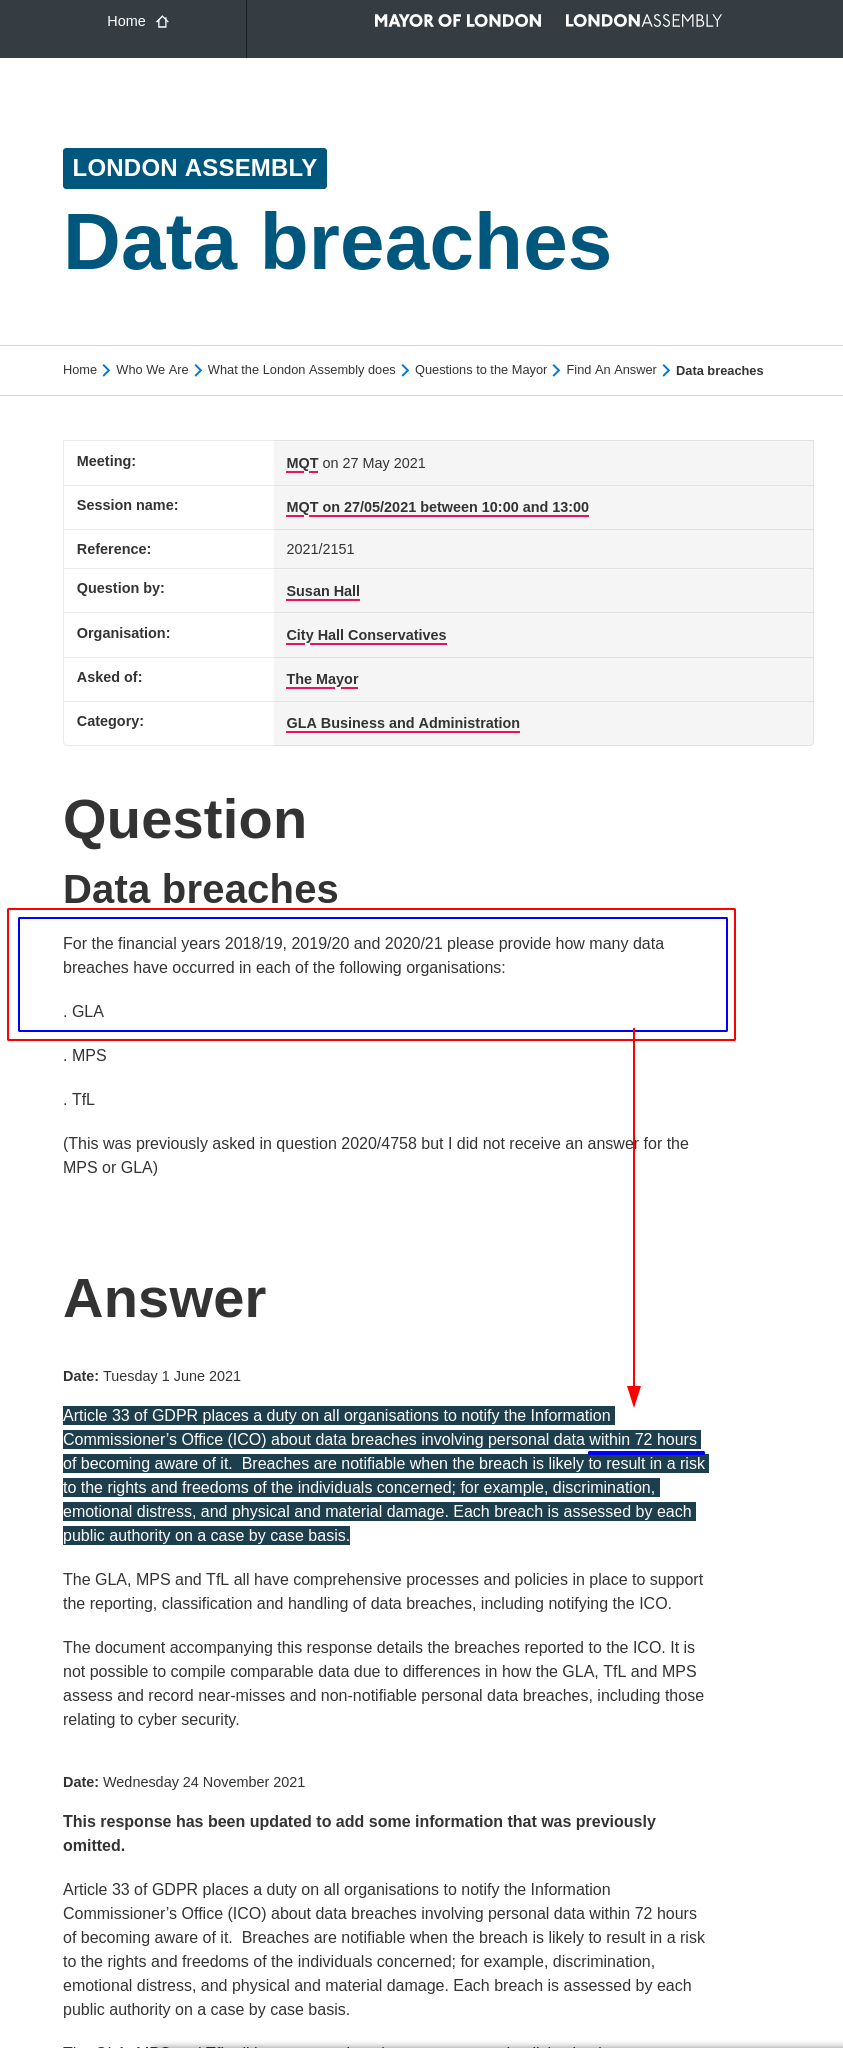
Data breaches’ handling policies/stance of GLA were not followed when I was there. Here they are in their own words:

GDPR, GLA, and Data Breaches

Meanwhile in the news:

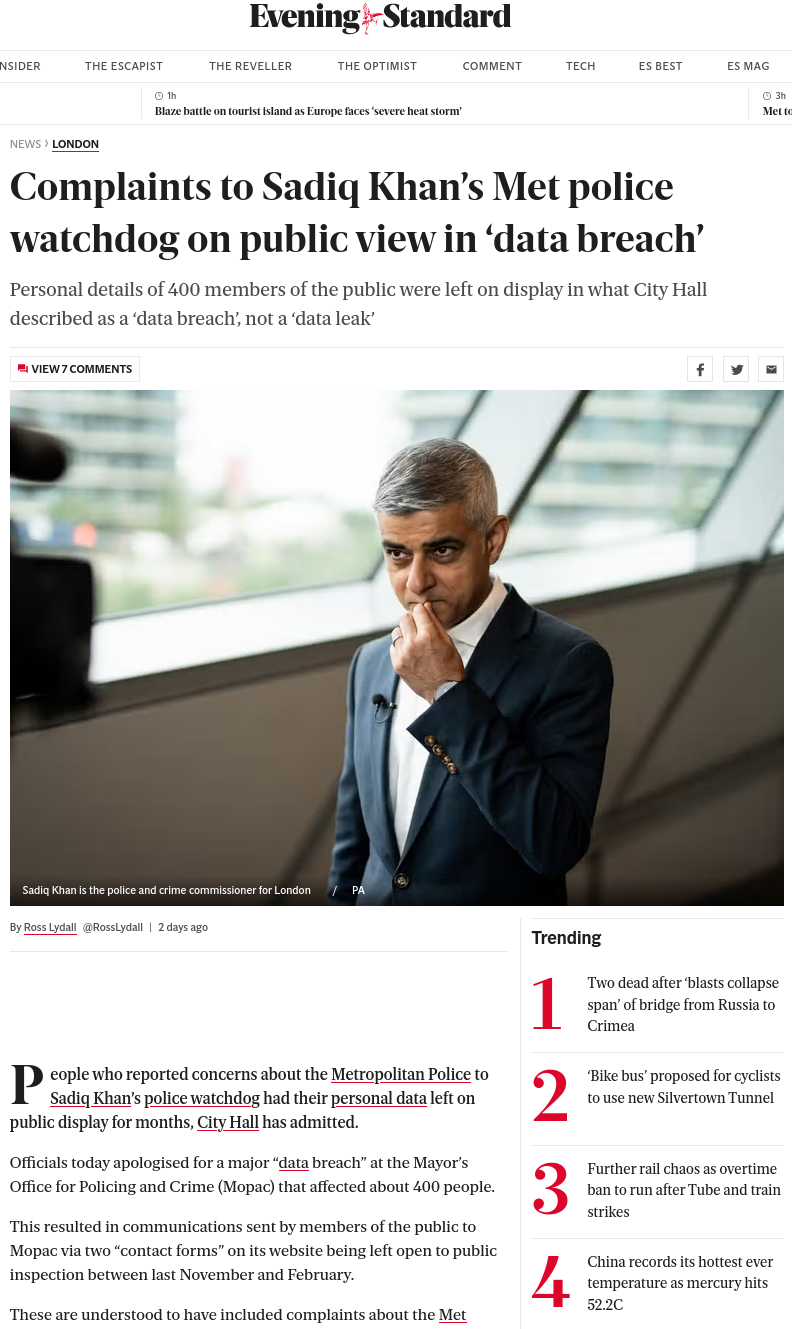
Complaints to Sadiq Khan’s Met police watchdog on public view in ‘data breach’

Also this past weekend:

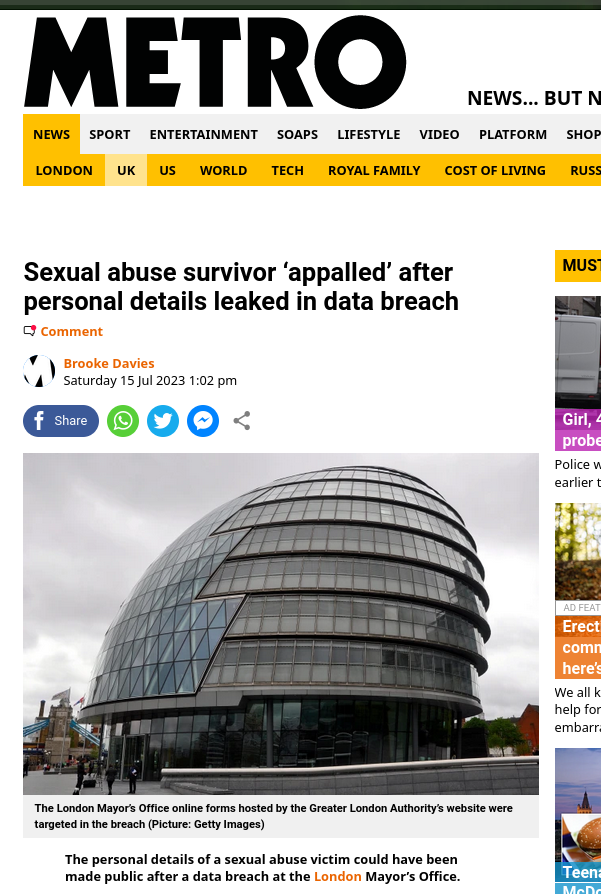
Metro: Sexual abuse survivor ‘appalled’ after personal details leaked in data breach

Summary: This past weekend Greater London Authority’s managers came under fire for mishandling of data (this went on for months!) and it wasn’t even the first time; usually they keep quiet about such things and hope nobody will notice while IT people — including Sirius ‘Open Source’ — are retroactively ‘fixing’ these issues

Monday, July 17th, 2023, 7:06 am

The Resonance Centre in Manchester

I think it’s fair to say many people dropped their gym-going habits after COVID-19 had erupted and lockdowns began, either for health reasons, financial reasons, or the gyms simply shutting down (many did). Almost exactly two years ago The Resonance Centre opened not far from us, so we went to have a look at it turned out they not only do yoga classes but a whole bunch of other things. They’re also promoting veganism.

Their Web site is under-developed at the moment, so I thought I’d drop a plug and prematurely an endorsement of sorts. The Resonance Center is near to Manchester City Stadium, just a short (about 10-minute) stroll along the lovely canal. The staff there is very friendly.

Here’s how to get there from Manchester City Stadium without all the traffic.

The  Resonance Center is near to  Manchester City Stadium

Monday, July 17th, 2023, 12:06 am

The Long History of Greater London Authority Data Protection Blunders

Summary: Data security and system security at Greater London Authority’s Web site haven’t been good; today we share just a couple of examples which help refute statements issued by Greater London Authority after a scandal that had made it to the mainstream media

MY! It really takes a liar to progress to management. The better the liar, the higher up the role.

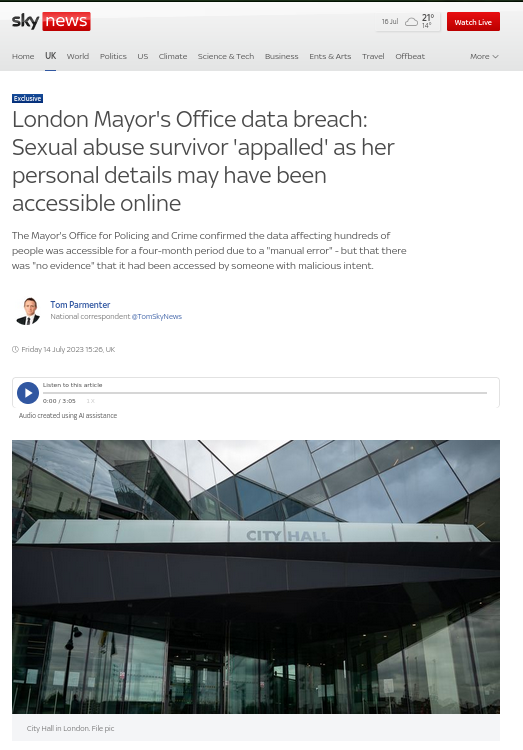
As I mentioned the other day, there’s somewhat of a blunder since Friday when the news broke:

London Mayor's Office data breach: Sexual abuse survivor 'appalled' as her personal details may have been accessible online

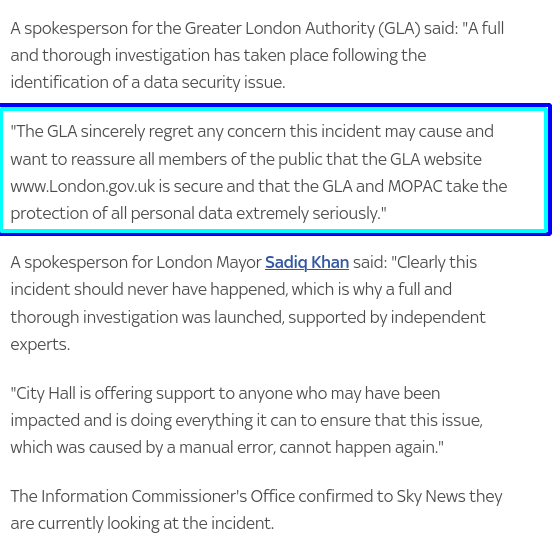
The following conspicuous statement is worth assessing, as I was working on the sites (various aspects, some microsites too) for 9 years.

GLA security assurance

You would expect them to say that, wouldn’t you?

As I said on Saturday morning, this has deja vu written all over it.

to give one example (there are more):

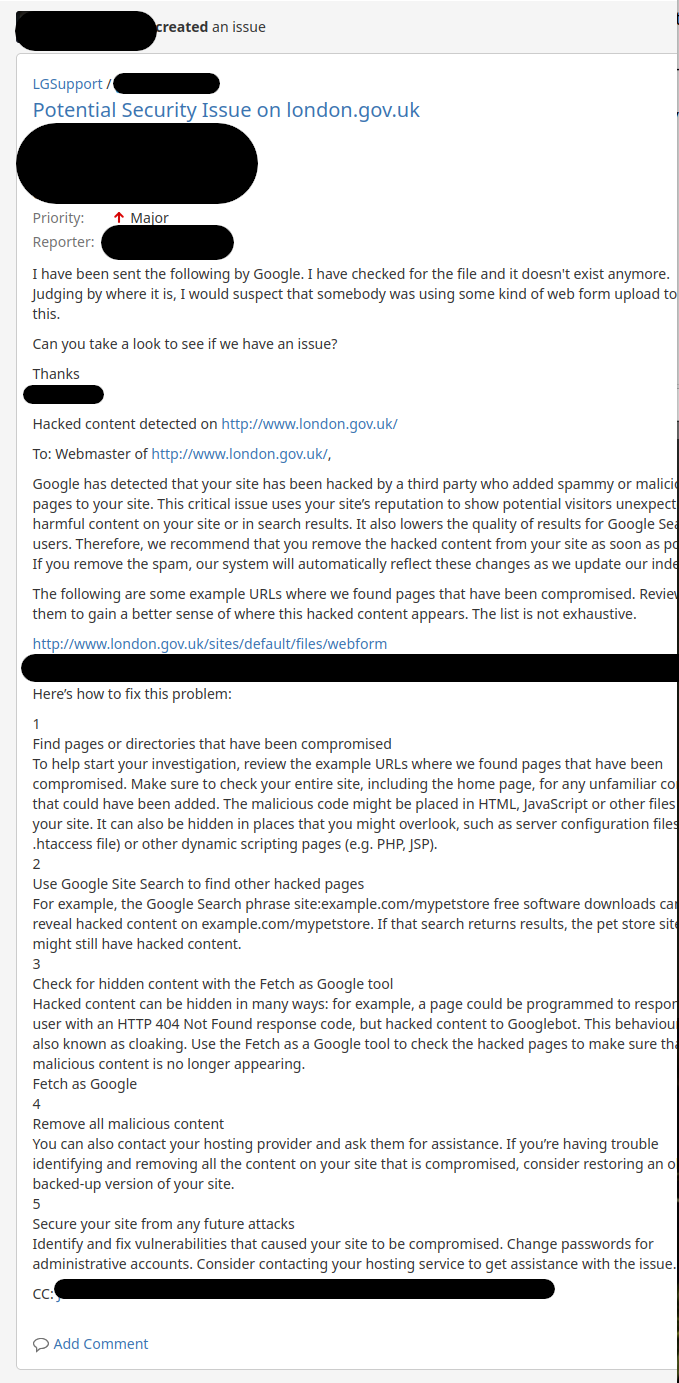
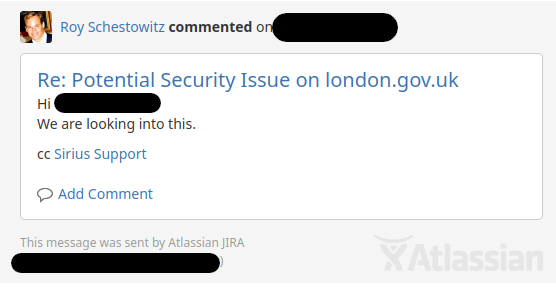
GLA: Google security alert

GLA security issue

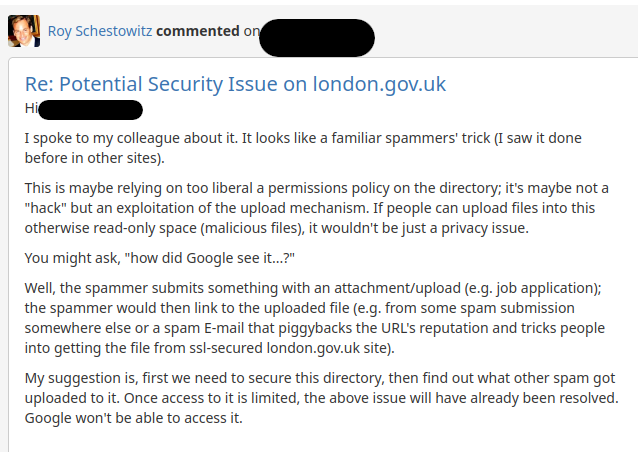
It wasn’t Sirius stuff (and certainly wasn’t me) who configured those terribly buggy forms.

GLA: Drupal access

GLA: Drupal permissions

As lying bosses at Sirius might say, “it doesn’t look good…”

It’s not the fault of Sirius either, at least not in this case.

The worst part of it is, as far as I’m aware GLA never publicly reported or disclosed this incident (sometimes this is legally required upon discovery or within a number of days, including informing those potentially affected, like people with their identity cards uploaded and widely available to the general public).

This isn’t the only such example.

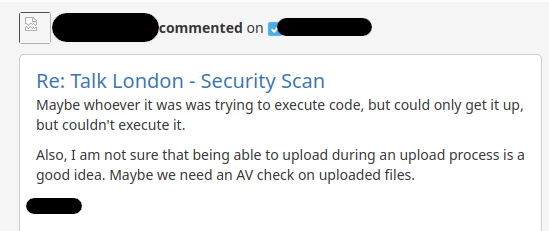
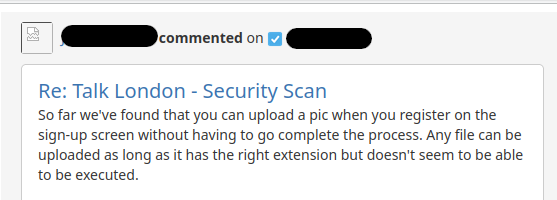
2 years later even malicious scripts/programs could be uploaded. It was only detected after it had happened. Here are some fragments of old messages:

GLA: can uploaded malware

GLA: any file uploaded

This is a penalty for not scanning/sanitising uploads/input.

Why am I publishing these (redacted sensibly)? Because lying is wrong and privacy problems are the problem, speaking about them is not the problem. It is the moral thing to do — to point out it is a repeat offender so to speak. There is an obligation here to debunk false assurances, as this has gone on for years already.

Sunday, July 16th, 2023, 2:51 pm

On the Greater London Authority Data Breach With Sex Abuse Victims’ Personal Details

Video download link | md5sum 65e2f74fa8f4c609f78e27dd7bf22983
Greater London Authority (GLA) Breaches Not Surprising
Creative Commons Attribution-No Derivative Works 4.0

Summary: The biggest clients of Sirius ‘Open Source’ included Greater London Authority, or GLA for short; GLA is making some shy and bashful faces right now, as there’s negative publicity after a damning incident

THE account sharing (mal)practices at GLA were noted here before. We often shared usernames and passwords (one colleague even sent passwords in plain text by GMail) and last year I cautioned GLA that LastPass had been breached and that Sirius kept GLA passwords in there. The vault was never safe and I protested against the use of LastPass repeatedly for several years (the liar would not listen). I habitually complained about bad security practices and only in 2022 or thereabouts we finally had individual UNIX accounts on the gateway machine rather than a shared account. Imagine the company bragging about ISO compliance while doing all that.

The video above focuses less on account sharing and instead talks about the site, including Drupal. In the distant past we already had severe permission issues (these were pointed out internally), but it remains rather baffling if not flabbergasting that names of sex crimes victims somehow ended on the public Web site. They should not be on any site at all. I explain the Microsoft-centric workflows and how they contribute to the risk. Poor security practices and a lack of proper protocols made the current blunder more or less inevitable. Cowboys shooting from the hip is no way to run a site of a city as important as London.

Friday, July 14th, 2023, 1:36 pm

Bad Management Ruining Canonical and Sirius ‘Open Source’

Video download link | md5sum 1df78d5342750f6e4e11cfa4536aa0da
To Developers, Canonical Not the Same Anymore
Creative Commons Attribution-No Derivative Works 4.0

Summary: A former client of my former employer (we supported postgres for them) has just lost a key developer and then resorted to ‘hijacking’ a project, exploiting the Contributor License Agreement (CLA); yes, Canonical is becoming more “closed”, just like Red Hat, so Free software proponents won’t stick around for much longer

THERE is a familiar sight. The symptoms strike a nerve.

A very short time after I had announced my resignation from Sirius ‘Open Source’ (that was before I even knew about the crimes, which I wrote about today in my personal site), someone from Canonical did the same thing and told a similar story. My wife joked that maybe he was inspired by us, but who can ever prove such a thing?

The video above discusses what happened this month and explains similarities to what happened last year at Sirius ‘Open Source’.

As a reminder, Canonical is a former client of Sirius. It shows it right there in the front page and footer, it’s not a secret:
Screenshot of Canonical as client Sirius

In any event, days ago Stéphane Graber (Launchpad member since 2005-09-26) resigned from Canonical and it doesn’t look pretty. Consider this original departure message and little other coverage that followed (any further updates clustered here in the future; we didn’t see this in LWN or Phoronix). To quote little coverage we found (from OMG! Ubuntu!): “Stéphane Graber has announced their resignation from Canonical after 12 years of working at the company, mostly on LXD. The decision follows news last week that Canonical has taken the LXD project in-house after years of it existing as a community endeavour under the Linux Containers (LXC) umbrella. Stéphane’s engineering expertise and enthusiasm for LXD (and containers in general) has arguably made them the “face” of LXD. In social media replies to their (somewhat unexpected) decision, many have commented on this and thanked them for their contributions and help over the years.”

“As a reminder, Canonical is a former client of Sirius.”He wrote many blog posts in the official Ubuntu site, albeit not in recent years (nothing since 2019).

“It’s a very bad situation for LXD / LXC due to Microsoft control and influence over Canonical,” one reader told us. We’ve recently shown just how close Canonical was getting to Microsoft, so maybe LXD work (and staff) was being chained to Microsoft’s proprietary surveillance grid.

From what can be gathered between the lines and elsewhere, there’s a leadership issue.

Stéphane Graber later added: “Canonical upper management apparently expects a community project to have the majority of its code contributed by external parties which LXD obviously didn’t. With a team of 10 or so to the engineers, Canonical likely contributed 90% or so of LXD’s code. I do strongly disagree about this being the main metric of the success of a community though…”

Gabriel Reiser responded: “Sad that they no longer understand the open source model and expect the community to get behind uninspiring leadership. LXD will live on. Canonical however, needs to find itself again.”

Maybe they hired the wrong managers, as the video points out. This happened in Sirius. When I left the company nobody in the management used Free/Open Source software. It had been like this for years already.

Comment or conclusion from my wife: “My personal view is, when the company changes its mission and vision, that’s a red flag, followed by the exodus of many, e.g. colleagues, managers, and even interns — and that is also another thing. Life in general isn’t going to revolve around work and money, that isn’t the essence of it. The feeling of freedom and fulfillment are most rewarding and that’s something which I haven’t felt for a long time until I left my job.”

Real-time Posts

Posts by @schestowitz

Retrieval statistics: 23 queries taking a total of 0.088 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|