Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Thursday, January 5th, 2023, 9:50 am

Data Contradiction Means Office for National Statistics (ONS) Began Shamelessly Lying About Number of Dead People

Weeks ago it said:

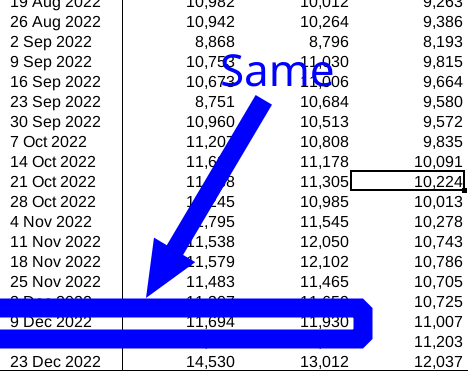
Over the Christmas period we will not be publishing Deaths registered weekly in England and Wales so the next publication will be available on the 5th of January and shall cover the weeks ending 16th and 23rd of December. Due to a processing issue, there has been an undercount of death occurrences in week ending 9th of December. Due to this the figures for week 49 will now be published in the next weekly mortality publication coming out on the 5th of January.

And this:

Undercount of deaths

Only a few minutes ago it released the numbers again. But they are the same!!!!!!!

Here:

Same undercount

In order to potentially save face for Rishi (unelected PM who pretends to be a GP now in some media photo ops) ONS delayed and delayed data. NO RELIABLE DATA ON DEATHS SINCE DECEMBER 2ND!!! And they did not bother to correct what they already admitted to be an “undercount”.

A new year’s resolution? Hide the dead? Undercount them?

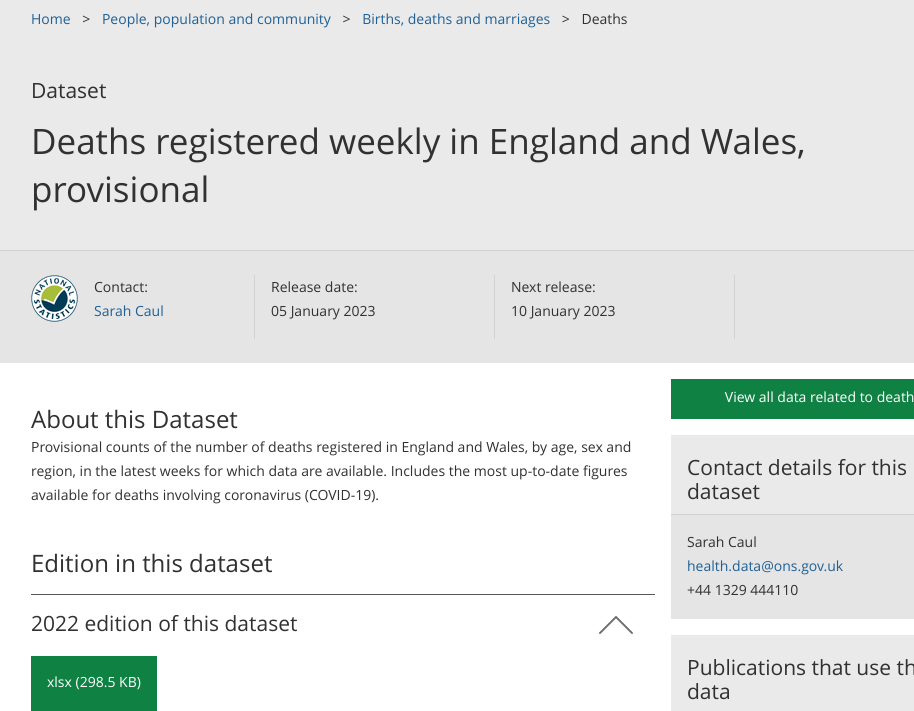
There is no notice in the site saying that they are still undercounting or that there is missing data. Sarah Caul’s update looks like this now:

Sarah Caul no notice

Sarah, does it take more than 3 weeks to ‘find’ those ‘missing’ death certificates? What on Earth is going on here? ‘Traffic-shaping’ of numbers? This is not acceptable. Taxpayers are paying to be informed; ONS says it’s not subjected to political pressure, but maybe that’s tacitly changing.

Thursday, January 5th, 2023, 1:59 am

COVIDiots: Too Confident

The risk of COVID-19 also varied by the number of COVID-19 vaccine doses previously received. The higher the number of vaccines previously received, the higher the risk of covid infection.

Download free high-res PDFs of the posters, download free copies of my two text books. Any donations using this link help the work of campbell teaching.

https://drjohncampbell.co.uk/

Order a hard copy Physiology book in the UK,

https://www.ebay.co.uk/itm/154973392319?mkcid=16&mkevt=1&mkrid=711-127632-2357-0&ssspo=K6raxMZrQnm&sssrc=2349624&ssuid=K6raxMZrQnm&var=&widget_ver=artemis&media=MORE

Vaccine doses versus risk of covid during the 3-month study period

One dose, 1.7 times more likely to test positive for covid

Two doses, 2.63 times more likely to test positive for covid

Three doses, 3.1 times more likely to test positive for covid

More than three doses, 3.8 times more likely to test positive for covid

So compared to the unvaccinated

1, x 1.7

2, x 2.36

3, x 3.1

4, x 3.38

P = 0.001 means 999 out of 1,000 likely to be a genuine result

That 99.9% likely to be a genuine result

Effectiveness of the Coronavirus Disease 2019 (COVID-19) Bivalent Vaccine

https://www.medrxiv.org/content/10.1101/2022.12.17.22283625v1.full

In 2020

(published in 2021)

Evidence that vaccines prevented covid infection

https://www.medrxiv.org/content/10.1101/2021.06.02.21258231v1

This was when the human population had just encountered the novel Severe Acute Respiratory Syndrome Coronavirus 2 (SARS-CoV-2) virus

Things Have Changed (Dylan)

Bivalent antigens

Original vaccine and BA.4/BA.5 lineages of Omicron.

(Approved without demonstration of effectiveness in human clinical studies)

(Approved without demonstration of safety in human clinical studies)

Background

To evaluate whether a bivalent COVID-19 vaccine protects against COVID-19.

Methods

Employees of Cleveland Clinic, n = 51,011

Cumulative incidence of COVID-19 was examined over the following weeks.

Protection provided by recent and prior vaccination was evaluated

First bivalents given, 12 September 2022

Three-month study

Results

Among 51,011 employees,

20,689 (41%) had had a previous documented episode of COVID-19,

42,064 (83%) had received at least two doses of a vaccine.

10,804 (21%) were bivalent vaccine boosted

COVID-19 occurred in 2,452 (5%) during the study.

(Pfizer 89%, Moderna 11%)

Risk of COVID-19 increased with time since the most recent prior COVID-19 episode

Risk of COVID-19 increased with the number of vaccine doses previously received.

Note, this is based on large numbers

Doses, 0 = 6,419 (12.6%)

Doses, 1 = 2,528 (5%)

Doses, 2 = 14,810 (45.9%)

Doses, 3 = 23,396 (45.9%)

Doses 4, 3,757 (7.4%)

Doses 5, 85 (less than1%)

Doses 6, 16 (less than 1%)

The bivalent vaccinated state

Was independently associated with lower risk of COVID-19 (HR, 0.70)

(over the 3 months of the study)

Leading to an estimated vaccine effectiveness (VE) of 30%

CDCs latest variant data

https://covid.cdc.gov/covid-data-tracker/#variant-proportions

Things Have Changed (Dylan)

Wednesday, January 4th, 2023, 4:34 pm

Sirius Bribing, Lying, or Both (in an Effort to Silence Disgruntled Staff)

Roy did not take my xmas bribe

Summary: After ‘sitting’ on his own letter for an entire weekend the CEO of Sirius ‘Open Source’ LTD (not the newer shell, “Sirius Open Source Inc.”) decided to send a harmful letter, incorrectly asserting that former staff cannot speak about the company (that’s a lie) and even trying to offer money (which he said was deserved but was never actually paid)

SHOWING THE FINAL LETTER from managers — a letter regarding our resignation (not sent the day it was written; it was sent 3 days later!) — we want to demonstrate what a self-defeating waste of paper that was. We dropped a hint on the eighteenth of December. Now we have the almost full thing (more personal/sensitive parts redacted).

Letter sent to Roy more than a week after leaving:

Roy's resignation page 1

Roy's resignation page 2

Roy's resignation page 3

Letter sent to Rianne over a week after resigning (she did not say or write anything; she had done nothing):

Rianne's resignation page 1

Rianne's resignation page 2

Rianne's resignation page 3

They basically offer money we’re not owed. Notice how they said the same to my wife.

Here are the now-reused screenshots (redacted):

Sirius ‘Open Source’ letter

Sirius ‘Open Source’ threat

It’s hardly even ambiguous.

So, Mr. former/ex-boss, if you are serious about us being entitled to holiday pay after leaving, then why were those payments not made to either of us? Dodging the liabilities to staff again?

If we’re not really legally entitled to such payments, then you basically just lied in an effort to bribe us into silence.

Either way, this is really awful. And leaving the company run by a liar is a case of “good riddance”.

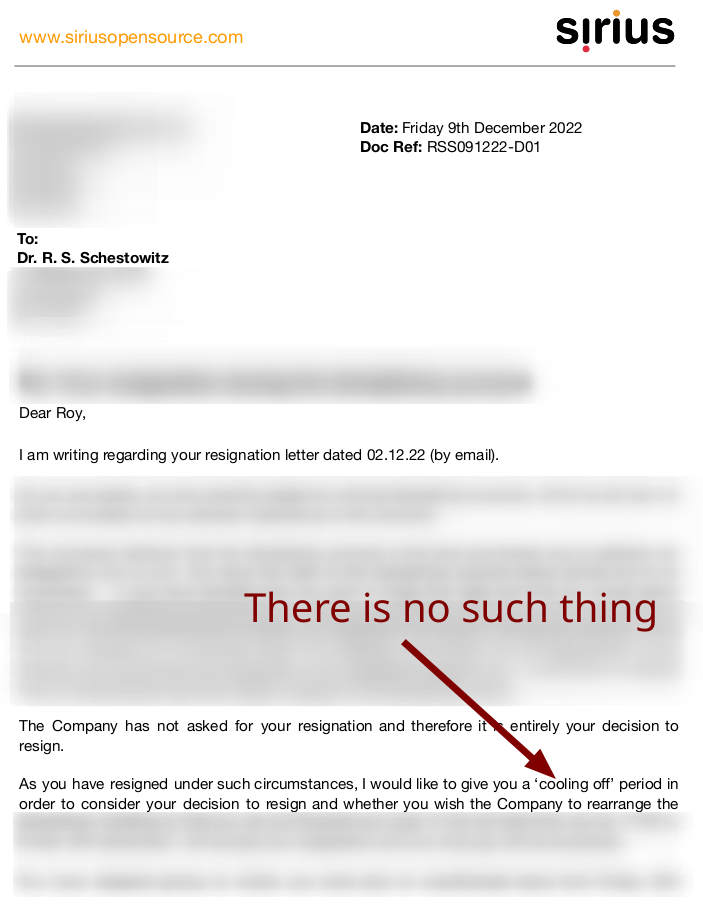
As noted above, there is no such thing as a “cool-off” period, so they are just improvising, making things up, flinging crap at the wall, hoping that something might eventually stick.

Regarding other stuff he’s trying to make up, a notice prior to resignation is inapplicable under the given circumstances. We left at the right time and they were legally obliged to respect our decision to leave, paying us for the days that we worked.

In this particular case, Sirius would be wiser to just say nothing. The above shows that the company either offers a bribe or is lying. It can’t be neither of those things.

Wednesday, January 4th, 2023, 5:08 am

The Shell Game of Sirius Open Source Inc.

Video download link | md5sum b197a526c46f992f5ebfa52d852853c9
Sirius Seriously in Trouble
Creative Commons Attribution-No Derivative Works 4.0

Summary: Sirius Open Source Inc. (or LTD or Corporation, among other past aliases) is running from one (egg)shell to another; we’ve provided a detailed summary of the company’s history and its darker secrets, seeing that it is abusing its own staff and lying to its valued clients

DESPITE veiled threats from Sirius ‘Open Source’ managers, we’ve finished publishing the entire report about the company and we will now proceed to covering several other scandals.

The video above is a relatively short discussion of what was posted yesterday, ranging from the dodgy new company (aside from a new shell in the UK there is another one in the US, named “Sirius Open Source Inc.”) to the company’s suppression of staff’s freedom of expression, more so after bagging money from the Gates Foundation (more on that later in this series).

Tomorrow we’ll show how the company lied to us in an effort to undermine this series. Either it lied or it tried to bribe us. Neither is particularly flattering.

Wednesday, January 4th, 2023, 1:15 am

Sirius Open Source Inc. as a Rogue Shell of a Failing Company

Sirius track record statement

Summary: Our report about Sirius ‘Open Source’ (as longtime insiders at the time) is available for reading by anyone who wishes to understand what Sirius ‘Open Source’ Inc./Limited/Corporation truly is

TODAY we publish a PDF version of the original report as sent to the company’s management a little over a month ago and just before my wife and I resigned. There are some typos in the document, which was prepared in a rush (just a couple of days’ work), but the series as we’ve covered it so far offers a lot more details, even some screenshots and better, additional context. It’s more suitably organised and adapted to an audience who knows too little or nothing about the company.

Download the statement/report (transmitted December 1st, 2022)

The series is far from over. Thus far we’ve only mentioned the stuff that was put in the report. We’ve since then remembered additional aspects and angles, which ought to be explained more properly, starting with the ‘gun-slinging’ by the CEO. Of course it backfired very badly.

Expect this series to last at least another month.

Tuesday, January 3rd, 2023, 5:20 am

Sirius Corporation Was Never the Same After Bill Gates Gave Money to the Boss Through a Newly-Created Shell in the US (First Client, Deal Signed Under a Non-Disclosure Agreement!)

Video download link | md5sum 8a72a6b59521aa3f57a2d3c616edc3af
Sirius Became as Dodgy as It Gets
Creative Commons Attribution-No Derivative Works 4.0

Summary: A look at half a dozen posts published here yesterday, ranging from security failures to dodgy business practices and status (or several shells registered and accommodated under false pretences)

THE past few years at Sirius ‘Open Source’ were somewhat horrifying not just to me personally; we’ve already shown some hard evidence that colleagues suffered abuse from managers only months after a new shell in the US had bagged money from the Gates Foundation at a very mysterious time (we explained this mystery yesterday). My wife suffered similar abuse — something which according to Tim Bray has some history when it comes to Microsoft.

The video above shows some very dodgy things the company (its management) was doing and saying in recent years. The video limits itself to stuff we covered in the past 24 hours alone. Later this month we’ll provide more detailed and ample evidence.

While it’s totally unclear whether there’s a correlation between the Gates money and the way the company was managed (denial would definitely be possible and there’s an NDA) the reality of the matter is, Sirius was gradually moving away from Free software — including infrastructure it had already had for more than a decade! In turn, the company was becoming several shells (at least 3) and at the moment everything is registered with some accountants rather than a real address of a director or an office.

This series will hopefully become a cautionary tale not just about openwashing companies (or formerly Free software companies). A lot of these things can happen and do occasionally happen in other “IT” companies. It’s important to know when to leave.

Tuesday, January 3rd, 2023, 2:48 am

When ISO Becomes Meaningless Paperwork

What if ISO knew the truth?

International Organization for Standardization (ISO) brag

Summary: There are no proper and truly compliance-driven procedures that are being followed, actively used, or even vaguely specified by poor leadership at Sirius ‘Open Source’; it’s all improvised, hugely deficient, not even remotely compliant, and changes are sometimes made retroactively due to lapses and mistakes (compliance or merely appearance thereof, albeit only “after the act”); eventually there are attempts to shoot the messengers — those who have actually cautioned about those concerning things for several years already

THE “Conclusion” part of the report (a document we’ll publish tomorrow as PDF) is included at the bottom of this post. Worry not, it’s not the end of the series, only the end of this report; we have plenty left to show and to explain after that. We’re eager to show to the world what Sirius ‘Open Source’ Inc./Limited/Corporation truly is.

As a teaser of sorts, consider how poorly the company was handling data and information. It was getting worse over time because skilled people were leaving the company, making way for the “Google is your friend” mantra. This aforementioned mantra was something along the lines of, “trust big companies”, you can give them any data we have. Trust them, they’re big! Sure, they also spy for a government.

Data of high-profile clients, both past and present, was naturally left scattered all over the place, sometimes even outside the country. And to give just one example (there are so many; some will be covered later this month and next month), colleagues have cognition reports and incremental/full load reports on local — as in personal and offsite — machines (this is indirectly related to patients’ data) with no protocol or guidelines for removing these. There’s potentially sensitive data on people’s machines at home and we’ve already witnessed mistakes made by the clients themselves (like patients’ names or similar data showing up by mistake/accident).

THIS SHOULD NEVER HAPPEN!

In a saner world, everything would be uploaded to a firewalled file server located on the client’s own network, accessible in some secure fashion, without the data ever leaving the network, not even metadata. But when a company like Sirius handles its E-mail via AWS and AWS is also the host of OTRS (ticketing), one is expected to just upload files to AWS and transmit the stuff over E-mail (i.e. open relays). No encryption. I was repeatedly told off for using PGP in my E-mails.

There are serious ramifications for data protection and adherence to law, as there are unpatched old machines and perhaps backups that contain such files — a ticking time bomb. And even way after they’re no longer a client (years later), the example above serves to show that the problem does not go away. Not even when the contract ends (or gets terminated).

The sad reality is that the company, Sirius (so-called ‘open source’), is terrified about clients finding out how reckless and incompetent the company gradually became. Clients simply come to assume the reputation earned in past decades persists to date. They’re trusting a company run by a person divorced twice, whose kids refuse to even speak to him. How can deep trust be established with people who (if they get caught) simply pretend nothing bad happened and instead of apologising would rather get aggressive, even combative, to cover up the abuse?

The text below mentions ISO, security incidents, and then the company’s attempts to shoot the messenger (who cautioned about those issues along with many other issues). The in-depth analysis of the witch-hunt will follow after this report is published in full (some time tomorrow).


Conclusion

To summarise, Sirius should simply admit out in the open: “we’ve deviated away from our mission,” and moreover Sirius ignores warnings about security (ISO deserves to know about phonies and posers at security).

Roy internally cautioned about this several times over the years. Later, when some providers suffers security breaches (as Roy predicted) Sirius neither reset the passwords nor left the compromised providers.

To reiterate what was stated at the start, what’s alleged here is factually correct and evidence-backed. No URLs are provided, but URLs can be provided shall they be requested. Brevity still matters and much remains to be told.

In regards to the weak accusations leveraged to avoid paying compensation to Roy and Rianne, here again is the gist of the underlying issue/s:

1. no due process
2. no evidence presented (or claims merely alluded to without context/link)
3. gross accusation inflation
4. guilt by association (identical letter, too)
5. the company has a history doing this to couples, e.g. one blind colleague based in Germany; it was very serious and it went to court (cost the company or its Directors — the founder and his wife — a lot of money, went on for a long time, settled at the end)

The document is far from complete. Roy and Rianne have documents, have screenshots, links to official documents from Companies House etc.

Real-time Posts

Posts by @schestowitz

Retrieval statistics: 23 queries taking a total of 0.102 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|