Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Wednesday, December 21st, 2022, 5:39 am

How Sirius Open Source Turned From a Company Into Just an Account

Video download link | md5sum 7fe1fe13ceb4d6a779380ededbafb8b4
Security Impermissible in Sirius
Creative Commons Attribution-No Derivative Works 4.0

Summary: Some years ago my employer was abandoning (piece-wise) its own infrastructure along with Free software, security, and privacy, in effect rendering the company a set of accounts in various third-party servers overseas (security breaches were routine but conveniently ignored)

THE company I left this month, Sirius ‘Open Source’, gave me a lot of abuse (like unjust threats) for merely doing what’s right and what’s legal. No person should be in such a position, but choices were limited during a pandemic and working from home is generally preferable, even if the working hours are quite insane.

A company that used to have its own telephony system and do conference calls over Asterisk (or similar) later became some Zoom or Skype or Google tenant, subjecting the company’s operations to total surveillance. A company that used to manage accounts with self-hosted OpenLDAP gradually started creating accounts in third parties like Slack and LastPass. No wonder system administrators left; their job was made obsolete and the roles had increasingly become almost clerical, not technical. Bad technology was chosen or outsourced to. It was all proprietary. No control, no room for learning, no customisation, and nothing to actually offer.

Tuesday, December 20th, 2022, 4:35 pm

In Sirius Open Source You Get Told Off — and Even Threatened! — for Minding Security and Privacy

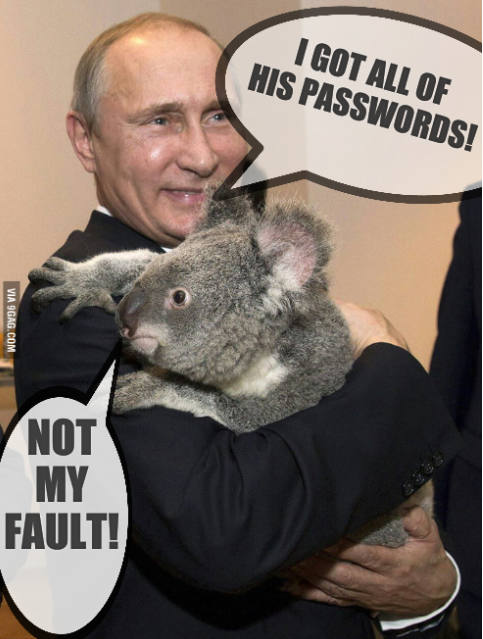
Putin koala: I got all of his passwords! Not my fault!

Summary: The Sirius ‘Open Source’ management made the decision (without any consultation with the staff affected) to outsource key operations to foreign, third-party entities that are subjected to the US government’s prying eyes and several of the National Security Agency’s programs; this affected clients as well (usually without their awareness, let alone consent)

THIS is the last part of the third section of a report I left with the company before leaving at the start of this month. There will be a lot more information about this scandal next month. Recent E-mails are appended below (with certain stuff redacted for privacy’s sake).

I cautioned about this repeatedly (for about 4 years) and suffered retribution, threats, and more. Nothing has improved since then.

As just a little sample, please see the E-mails at the bottom (recent); shared in the future will be some longer E-mails about this issue.

But first… the report.


The morale around that time was low, set aside COVID-19 becoming a growing problem, along with lock-downs. Roy noted that in order to comply with the law he cannot post clients’ details on the Slack network. So he chose to obey the regulations and the law, in line with security standards. Stuff like “hi” is probably considered OK and safe enough for Slack, but not addresses, passwords etc. Things have not improved since, as the final section notes again (with examples).

This long section, along with written messages as evidence, is very important. Bad leadership worsened the corporate climate and changed how people viewed the company from within, if not from the outside as well.

This document now proceeds to a discussion about the latest and maybe the final blow. The company already had capacity issues (not enough staff to cover shifts) and now it’s even worse.

Roy and Rianne hoped to prevent a ‘death spiral’ and ironically enough it seems like the company wants to accelerate its own ‘death spiral’, due to tactless, insensitive remarks.


One of many messages to that effect — messages which I was sending for years to highlight the problem. Of course nothing was done about this; usually there was not even as much as a reply. Hush hush as a company-wide policy…

This one is from August of this year:

Date: Tue, 30 Aug 2022 09:00:50 +0100
MIME-Version: 1.0
User-Agent: Mozilla/5.0 (X11; U; Linux i686; en-US; rv:1.7.6) Gecko/20050317
 Thunderbird/1.0.2 Mnenhy/0.7.4.0
From: Roy Schestowitz
Subject: Handover to Shift 2 (30/08/22)
To: [whole team]

[...]

https://www.darkreading.com/cloud/lastpass-data-breach-source-code-stolen

users need to change all the passwords they have there and not keep them
there if they value real security not paper mills.

Another one from August of this year:

Date: Thu, 11 Aug 2022 03:10:53 +0100
MIME-Version: 1.0
User-Agent: Mozilla/5.0 (X11; U; Linux i686; en-US; rv:1.7.6) Gecko/20050317
 Thunderbird/1.0.2 Mnenhy/0.7.4.0
Content-Language: en-US
From: Roy Schestowitz
Subject: Slack admits to leaking hashed passwords for five years
To: [whole team]
Content-Type: text/plain; charset=UTF-8
Content-Transfer-Encoding: 7bit

https://nakedsecurity.sophos.com/2022/08/08/slack-admits-to-leaking-hashed-passwords-for-three-months/

Does not surprise me at all. They only admit this because they got
caught, hence they need to spin this somehow, belittling the severity,
just as LastPass did after several blunders (it had suffered a breach).
The way forward is self-hosting and encrypting things (on server one
controls, not leasing).

Tuesday, December 20th, 2022, 3:52 pm

“It Is Estimated That Only 10% of Serious Reactions and Between 2 and 4% of Non-serious Reactions Are Reported.” (Follow-up)

Yellow card scheme, Don’t wait for someone else to report it

www.gov.uk/drug-safety-update/yellow-card-please-h…

It is estimated that only 10% of serious reactions and between 2 and 4% of non-serious reactions are reported.

Yellow card government site, just a click away

https://www.gov.uk/government/publications/coronavirus-covid-19-vaccine-adverse-reactions/coronavirus-vaccine-summary-of-yellow-card-reporting

As of 23 November 2022, (UK)

Pfizer/BioNTech, monovalent and bivalent

177,925 Yellow Cards have been reported

AstraZeneca

246,866 have been reported

Moderna, monovalent and bivalent

47,045 have been reported

Novavax

52 reports

Brand of vaccine was not specified

2,130 reports

Total reports

474,018

Overall reporting rate

Around 2 to 5 Yellow Cards per 1,000 doses administered

In the 28 days

Pfizer/BioNTech, + 2,499 reports

AstraZeneca, + 228

Moderna, + 1,099

Novavax, + 15

Brand not specified, + 154

For all COVID-19 vaccines

injection-site reactions (sore arm for example)

generalised symptoms such as ‘flu-like’ illness

headache, chills, fatigue (tiredness), nausea (feeling sick), fever, dizziness, weakness, aching muscles, rapid heartbeat

they may be reported more frequently in younger adults

Overall, our advice remains that the benefits of the vaccines outweigh the risks in the majority of people.

The benefits of the vaccines in preventing COVID-19 and serious complications associated with COVID-19 far outweigh any currently known side effects in the majority of patients.

https://wchh.onlinelibrary.wiley.com/doi/pdf/10.1002/psb.1789

Google YT guidelines

https://support.google.com/youtube/answer/9891785

Claims that an approved COVID-19 vaccine will cause death, infertility, miscarriage, autism, or contraction of other infectious diseases

https://www.gov.uk/government/publications/regulatory-approval-of-covid-19-vaccine-moderna/information-for-healthcare-professionals-on-covid-19-vaccine-moderna

4.4 Special warnings and precautions for use

Hypersensitivity and anaphylaxis
Anaphylaxis has been reported in individuals who have received Spikevax.

Close observation for at least 15 minutes is recommended following vaccination.

Myocarditis and pericarditis

There is an increased risk for myocarditis and pericarditis following vaccination with Spikevax.

Few days, primarily occurred within 14 days,

more often after the second dose,

more often in younger males

risk profile appears to be similar for the second and the third dose

Available data suggest that the course of myocarditis and pericarditis following vaccination is not different from myocarditis or pericarditis in general.

Healthcare professionals should be alert to the signs and symptoms of myocarditis and pericarditis.

Vaccinated individuals should be instructed to seek immediate medical attention if they develop symptoms indicative of myocarditis or pericarditis,

such as (acute or persisting) chest pain, shortness of breath or palpitations following vaccination.

Healthcare professionals should consult guidance and/or specialists to diagnose and treat this condition.

Who can get a COVID-19 vaccine

https://www.nhs.uk/conditions/coronavirus-covid-19/coronavirus-vaccination/coronavirus-vaccine/

Everyone aged 5 (on or before 31 August 2022) and over can get a 1st and 2nd dose of the COVID-19 vaccine.

People aged 16 and over, and some children aged 12 to 15, can also get a booster dose.
Hypertension after COVID-19 vaccination

https://pubmed.ncbi.nlm.nih.gov/34985455/

Italian research

Tuesday, December 20th, 2022, 10:22 am

Office for National Statistics Unable to Publish Statistics That Show Far More Deaths Than Usual

A “dog ate my homework” moment?

After much waiting, and maybe a dozen page refreshes*, we finally get this:

Over the Christmas period we will not be publishing Deaths registered weekly in England and Wales so the next publication will be available on the 5th of January and shall cover the weeks ending 16th and 23rd of December. Due to a processing issue, there has been an undercount of death occurrences in week ending 9th of December. Due to this the figures for week 49 will now be published in the next weekly mortality publication coming out on the 5th of January.

Are these numbers reliable?

Undercount of deaths

Can they blame Microsoft Excel? Either way, vigilant citizens are being left in the dark for about 3 weeks**. How hard can it be to just count death certificates (no classification needed)?

________
* I’ve been very eager to see these numbers. We see reports about COVID and hospitalisation surges.
** It’s hard not to feel like they may be ‘hiding’ the dead now (the totals at least). Delaying the information? We have a vaccine crisis, virus crisis, freezing wave etc.

Tuesday, December 20th, 2022, 5:43 am

There Are Now at Least Three ‘Shell Companies’ for Sirius ‘Open Source’

Video download link | md5sum 2559ad3e58655ae8f53c6926a800bc30
The Sirius Open Source Shell Game
Creative Commons Attribution-No Derivative Works 4.0

Summary: Sirius ‘Open Source’ is trying to dodge liabilities; in the process it misleads staff and bullies staff, leading some colleagues to abrupt departures and others into mental and physical health problems

THE company that my wife and I left earlier this month no longer has an office and no longer pretends to have an office, either. About 7 weeks ago the address was changed for the second time in a month. The current address isn’t even the company’s own.

The legal status of the company is unclear or barely verifiable. People who ask about it receive evasive if not aggressive replies. The video above goes through the latest 3 posts about the company. This hopefully serves as a bit of a cautionary tale. Do not work for companies like these. Spot the signs.

Tuesday, December 20th, 2022, 1:31 am

Staff Suffered Health Problems Due to Bullying by Management at Sirius ‘Open Source’

Aside from the bizarre working hours, there were other factors.

Koala Preparing For Shift

Summary: Abuse and bullying by management at Sirius ‘Open Source’ caused health problems for some staff; this is no laughing matter as there can be legal ramifications

THIS series is about halfway through now. It has only been prepared for a number of weeks and more material is being added as we go along.

Speaking for myself, I never took sick leave (or time off work for illness) in my entire time in the company. The same goes for my wife. But colleagues have had different experiences. One was rushed to the hospital with COVID-19 (from which he never fully recovered) and another suffered from abuse by managers. This abuse was causing health issues, in effect harming the health of staff, as we shall show much later in this series. This is what happens when completely untrained (not merely insufficiently or improperly trained) people are assigned or entrusted to manage a company with workers who are difficult to recruit and then retain. Skilled and experienced staff is very hard to find and keep.

As a reminder, managers at Sirius aren’t there for their skills but for nepotism. They posses no relevant skills and clients can notice this. Of course it can in turn lead to contract cancellations and non-renewals.

Here’s the relevant part of the report:


In later years the nepotism (to be expanded upon in the final section) became apparent. Some people were basically implicitly shielded from criticism.

For instance, one colleague was often late to the shift and did not apologise. Her partner did the same thing — basically came online almost half an hour late without apology. This is abject disrespect for colleagues, even people who have been in the company for much longer than them. The three-way relationship involved here will be explained later.

The above examples are merely a small subset and some are based on distant but accurate recollections of a rather dark era of distress. When a conceited manager is accusing, without any actual evidence, people of “cooking” while on the job it doesn’t sound like management but just an attempt to shame staff. As an aside, it was often unclear what the management itself was doing (if anything substantial at all). There was a sentiment that some management people colluded and perpetrated schemes against individual members of staff, not limited to Roy and Rianne. This often backfired. There were also examples of retaliation attempts. One common tactic, which can be witnessed outside the realm of high-tech as well, is to psychologically manipulate or assign people nonsensical things, e.g. asking then to perform totally meaningless jobs that don’t yield anything at all and don’t improve but rather worsen the service, encumbering staff, never to be checked by anyone (as if just to waste time). This happened in Sirius too.

The hypocrisy was not just routine; it was a new standard, e.g. reprimanding people for not picking up the phone fast enough even when there were upstream technical faults (supplier) or when Reception was far slower to pick up the phone, if at all. This sort of hypocrisy or these attempts to shame staff are akin to guilt tripping. Healthy work environments would weed out such behaviour outright.

Tuesday, December 20th, 2022, 12:07 am

“It is Estimated That Only 10% of Serious Reactions and Between 2 and 4% of Non-serious Reactions are Reported.”

Real-time Posts

Posts by @schestowitz

Retrieval statistics: 23 queries taking a total of 0.092 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|