Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Saturday, December 10th, 2022, 3:04 pm

Security Problems at Sirius ‘Open Source’

Video download link | md5sum ac3236ee212e511a0874c1eecac90893
Insecure About Security Status
Creative Commons Attribution-No Derivative Works 4.0

Summary: At Sirius ‘Open Source’, which we left 8 days ago, security had been neglected for years; at the moment the company brags about “ISO” and other three- (or four-) letter acronyms, but many of the basic practices are conveniently ignored

THE sad reality is that when it comes to security many people and corporations prey on perception rather than reality. They indulge in what they can tell the public (or clients). For instance, Microsoft uses media “plugs” to pretend Microsoft is some sort of security expert with many security gurus whilst actively pursuing back doors for the NSA and others. In my latest job (almost 12 years) I witnesses customers suffering security breaches; we’re not meant to tell people about clientele covering up such incidents because it might result in fines or erosion of confidence.

orse yet, highlighting that some company is failing when it comes to security (as happened at Twitter earlier this year; their security chief had become a whistleblower) is seen as the real problem; in healthy workplaces the problem would be security lapses, not the people who talk about them.

Aside from the above video I still have plenty to say and to show (without infringing the privacy or people or naming any companies).

Saturday, December 10th, 2022, 10:04 am

Patching My Work PC (at Sirius Open Source) ‘Absolutely Unacceptable’?

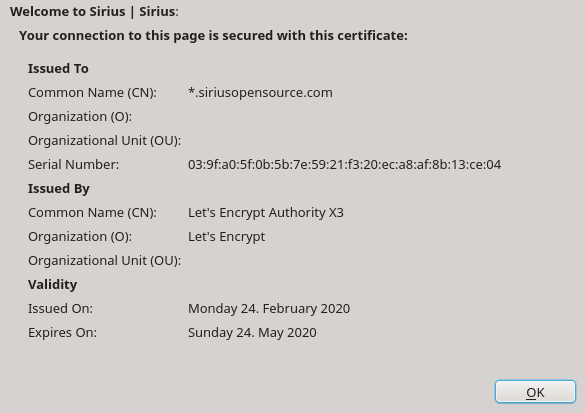
Sirius certificate

Summary: In Sirius ‘Open Source’, neither Open Source nor security got taken seriously enough. Siriusly! And one cannot point this out to managers as this infuriates them (it harms a false perception they’ve long cultivated).

TODAY we turn our attention to bad security practices, including poor privacy and unbridled outsourcing of Sirius. There will be numerous parts about these aspects and we’ll provide some examples in the future when dealing with proprietary software, introduced by the company itself while tearing down its very own Free software-based infrastructure (which had been put there when the company still had geeks in the office; heck, the company used to have an actual office!).

Suffice to say, patching is part of the work, including patching one’s own machine. Anything else would be irrational (like blasting people over “commuting” time) because security starts in one’s own domain. And yet, I was being told off by the company’s founder for patching my PCs while I was on shift despite the fact that there are several such machines (if one encounters an error, then one can rely on another machine) and this is about actual security.

It took me a while to find E-mail regarding this, as it dates back nearly 4 years. My redacted response below:

I have just caught up with E-mail (resting and other things since 9am).
Sorry for the delay in responding.

Roy,

I have read your shift’s handover notes where I find this from you:

“Quiet shift, so I took the time to update my whole system. Something broke nagstamon for me, briefly, but I managed to fix it. In the meantime I used the Nagios/Icinga Web interface.”

I use 3 laptops in parallel to do my job, so this was one in three and Nagios remains accessible regardless. nagstamon is an alternative to it (sound alerts) and I wanted to bring it up to date for security reasons. As I do often, to avoid breaches.

This is *absolutely unacceptable*.

If I cannot observe systems that are monitored and supported, it’s not “unacceptable”. It’s still very much necessary. But still, looking back, there are many serious (Sirius) issues that were shared in the report below (more to come in the next parts).


Acronyms Lingo

Speaking of “GDPR” or “ISO” without even grasping the meaning behind laws and regulations is “cheap talk”. Without comprehension of the issues, this boils down to ‘name-dropping’ (like “GDPR” or “ISO”). Currently, the company would gladly take technical advice from people who openly admit they don’t care about privacy. So instead Sirius falls back onto formalities and processes rather than any real grasp of the underlying issues. Sirius track record will be demonstrable based on recommendations from past clients; with or from at least two clients we might only get an alarming reminder that their systems suffered a security breach while we supported them. The clients’ names are, as usual, omitted here, but this is very well documented. There may have been more security incidents that were hidden or concealed both from clients and from Sirius staff. Considering the atmosphere of secrecy and hostility towards inquisitive staff, it seems likely more incidents occurred but weren’t reported at all (or reported very selectively).

Speaking of formalities and processes rather than actual substance, the company Sirius was pursing ISO certification only amid some issues with NHS and its highly sensitive medical data — including several incidents staff witnessed where people’s (patients’) privacy was accidentally compromised, either by Sirius or by the client (personally identifiable data divulged). To make matters worse, many times data was not being shredded like it was supposed to and the client complained. If better leadership was in place, this would not have happened, jeopardising the credibility of staff.

Account Management Practices and Data Sovereignty

With quite a lot of clients, and several can be vividly recalled, Sirius failed to remove access credentials (or accounts) for staff that had already left Sirius. ‘Low level’ staff cannot access systems at a level of user management, so this was demonstrably a ‘high level’ failure. Sometimes clients complained about such gross incompetence (if clients could even figure out who still works for Sirius; remember that Sirius misled them, as shall be noted again later) and potential security breach by former and possibly disgruntled Sirius staff, but nobody (as far as we know) was being held accountable. The aforementioned sections noted that accountability only ever works in this hypocritical and vertically-inconsistent fashion. Double standards became the new company standard, enshrined covertly but not formally. Managers never offered the courtesy of taking full responsibility. Too much pride to acknowledge mistake and lapses.

As the above shows, there are endemic problems caused by mismanagement or a lack of charismatic-yet-humble leadership (maladministration), maybe even a lack of staff that possesses ample experience managing a team of more than one person. These are very essential skills which mandate suitable recruitment. It may not be cheap, but it is vital.

Sirius has user credentials scattered all over the place, not all in OpenLDAP as done in the past (when more competent people managed the company’s infrastructure). This will, inevitably, result in epic blunders. That keeps happening. Again and again. In fact, user credentials management at Sirius has been partly outsourced to third parties — a taboo subject. No more GOsa, go USA (most data and authentication sent across the Atlantic).

The motivations seem petty, e.g. sharing accounts to save money despite clear security requirements that exist to explicitly not do this. Is ISO being treated as merely a box-ticking exercise, not followed up by any potent audits? If so, are we entitled to brag about some ISO compliance? Any time Roy attempted to bring up the subject the management became paranoid and threatening. This sort of resistance to ethical and moral objection would be strongly discouraged in companies capable of self-appraisal.

A colleague once mentioned in an E-mail that some colleagues may have needed to share an account with another person, all in the name of saving money. This kept happening for years despite such ISO requirements supposedly being fully in force. Account sharing was sometimes imperative, as individual accounts did not exist. In other words, all colleagues use the same username for some tasks; sometimes this was only belatedly addressed, partially and virtually post hoc.

Password management in the company has long been a painful affair. From non-secure connections to a lack of VPN for access to passwords the company moved to outsourcing. This was a case of “bad optics”, pragmatic issues aside. Sirius could self-host similar software that was Free and Open Source software, but the company had a mindset of outsourcing almost everything to proprietary offerings from another country. As noted separately, Roy raised alarm over this several times, noting or pointing out actual data breaches of a very large scale, but no action was subsequently taken. The assurances were empty and arguably arrogant — a refusal to listen to vigilant security experts who extensively covered those issues for decades. Asking a company itself whether it suffered a security breach and what the severity truly is like asking an American president what happened in the Oval Room.

Friday, December 9th, 2022, 5:54 pm

When Colleagues Lie to Clients (Sirius Corporation)

Video download link | md5sum 1c4d7edce11724db5d55abfa26d673b2
Sirius Compromise of Integrity
Creative Commons Attribution-No Derivative Works 4.0

Summary: Sirius ‘Open Source’ has resorted to finger-pointing that distracts from the real culprits and covers up the real issues; a week ago I left my job after it had become too much to bear

Integrity of staff and reputation of people in the company where I worked apparently does not matter. For instance, lying to clients is an ethical breach, no matter how profitable it may seem at the time. Some of these clients are themselves unethical, but we don’t wish to name clients in this series. We only focus on Sirius ‘Open Source’ or Sirius Corporation.

The video above goes through the latest two parts of the series, which cover two aspects from the report we had left a day before resigning. There’s much to be said about the Code of Conduct-like nature of some of the policies; never dare accuse management of lying, even if it is objectively lying. The issue or the pesky person will be perceived to be anyone who opposes lies.

Friday, December 9th, 2022, 1:38 pm

Sirius Corporation’s Openwashing

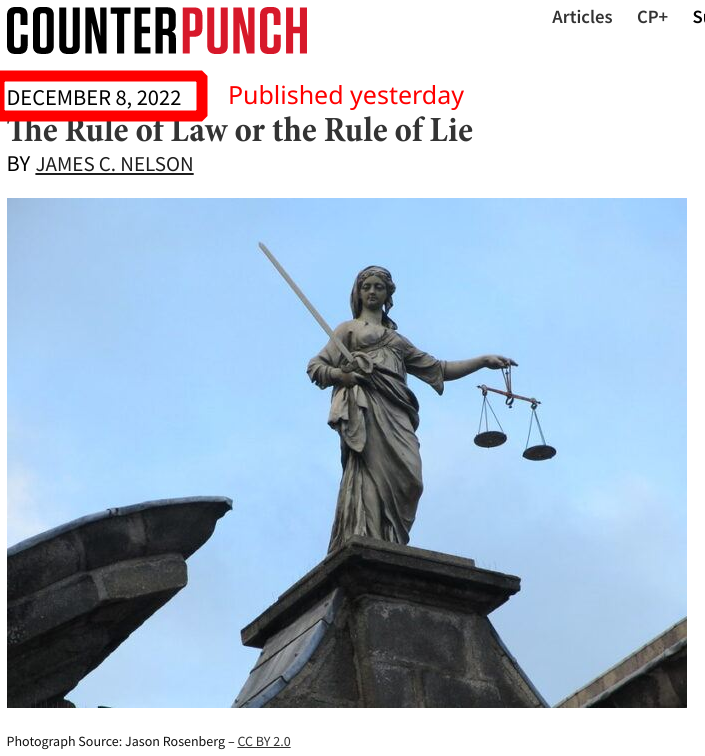
Published yesterday: The Rule of Law or the Rule of Lie

Many countries throughout the world strive to uphold the rule of law–where no one is above the law; where everyone is treated equally under the law; where everyone is held accountable to the same laws; where there are clear and fair processes for enforcing laws; where there is an independent judiciary; and where human rights are guaranteed for all.

Summary: Sirius ‘Open Source’ is still the official name of the company, but the company isn’t really ‘Open Source’ anymore; it’s not a viable company either, it’s run by only a handful of people

THE previous part of the report was entitled “Rules for Thee and Not for Me”, hence the above article. Deception and misapplied rules (or selectively enforced rules) became all too common at Sirius ‘Open Source’, a company we left exactly one week ago. It was too much to bear and criticism had become impermissible. Colleagues were compelled to lie to clients, which had become less and less ethical. Sirius itself was rapidly moving away from “Open Source” (the words in its own name!) or abandoning Free software; there was no room for debate or discussion about that.

Below is the relevant part of the report we left last week (internally, just before leaving).


Openwashing Ltd.

It may seem absurd that a CEO of “Sirius Open Source” uses only Non-Open Source software, also known as proprietary software, i.e. in practice he rejects Open Source (championing macOS, Chrome and not Chromium, lots of “cloud” things that are proprietary and exceedingly privacy-infringing), but this is what we have come to expect in a company building a facade based on past branding/reputation rather than the present. This point was covered earlier.

As an aside, lately the company posted links to anti-FSF defamation tabloids via the company’s Twitter account (Roy and Rianne did not comment but only took note), even though 1.5 decades earlier the company had financially supported the FSF. What happens when a company does not understand what it sells it may end up advocating Windows/WSL (helping Microsoft’s attack on GNU/Linux) or even using Windows with some ‘Linux’ thing in VirtualBox instead of the real thing? Welcome to Openwashing Ltd. formerly known as Sirius Open Source. There might even be some Open Source people inside the company. Might. Maybe…

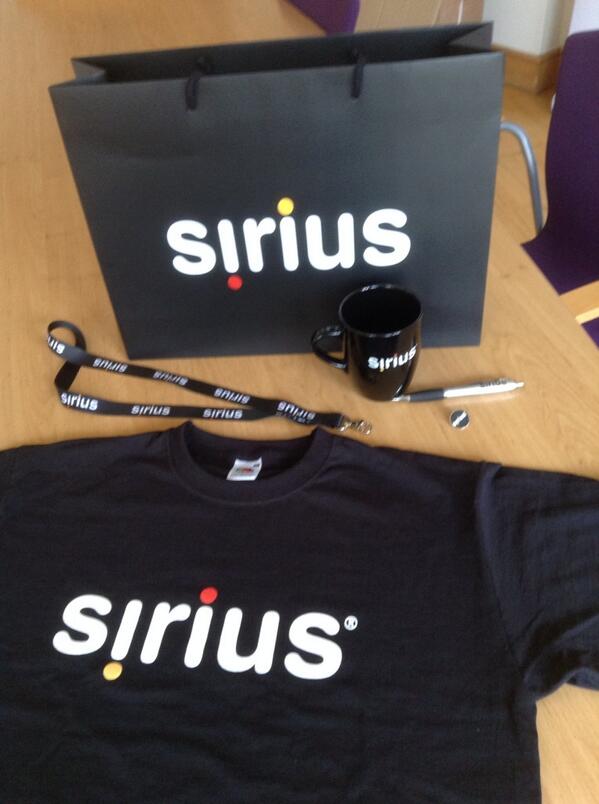
Sirius Open Source swag“Sirius Open Source” should be about more than the branding. People who actually use Free/Open Source software know that it is doable and know how to implement as well as recommend it (like the founder did; he gave many talks on the matter). Contrariwise, people who don’t use Free/Open Source software simply insist it’s not doable and sometimes say things like “this is just how the world works”. This kind of defeatism paralyses a company that built its whole image around “Open Source” (even paying to advertise itself accordingly), which needs to be championed for ‘Team Sirius’ to distinguish themselves (there’s plenty of competition; niches or sub-segments are simpler to complete for). Sirius as a company must not resort to false marketing, using the brand “Open Source” while in fact openwashing, neither caring about freedom nor using an OS (operating system) that adheres to freedom or autonomy and sometimes sends a lot of sensitive data to firms in foreign states. That includes some of the core clients’ data.

Thursday, December 8th, 2022, 5:18 pm

Managing or Bullying Staff at Sirius ‘Open Source’?

Sirius ‘Open Source’, where bullying and unwarranted bollocking against ‘low-level’ staff became the ‘norm’.

Sirius ‘Open Source’ talk

Summary: Sirius was abandoned a week ago (my wife and I resigned with immediate effect), leaving a skeleton crew that’s about 50% ‘management’ (barely qualified or not qualified at all) and 50% ‘low-paid’ geeks (what’s left of them); guess who’s blaming who and who always gets punished

IMAGINE working for a company that’s not only breaking rules but also lying to clients and lying to staff. It has long reminded me of the EPO and I planned my exit for a long time. Pandemic wasn’t a good time to leave (especially a job done purely from our own home).

Yesterday and the day before that we illuminated the payslips and pension scandals, elucidating further with some meticulously-redacted examples (safeguarding people’s and clients’ privacy, even the pension provider’s name).

As we shall show later in the series, when mistakes are made by management there’s no admission of guilt, no responsibility, just deflection of blame along with breathtaking cover-up attempts. No sane person would tolerate that for much longer. I challenged this and spoke out against this many times (internally). There were attempts to spin my polite communications as lacking in manners (totally false). This is a typical Code of Conduct-like manoeuvre. In practice, it helps corporations and heads of corporations (e.g. shareholders, managers) suppress messages from critics.

From the report issued and sent at the start of this month:


“Rules for Thee and Not for Me”

As noted above, with further examples to come later, management was given the liberty to make up all the colourful excuses and no disciplinary procedures were pursued when managers failed to do very essential and sometimes utterly simple jobs (sending payslips is very trivial). In the commercial world this qualifies as gross incompetence. As shall be explained later on, the management oftentimes seems or feels like it’s “missing in action”, like spending several weeks stalking staff, fishing for ‘dirt’ online and inflating or taking out of context the content (which does not infringe privacy, let alone company policies).

Companies worldwide must recognise that every staff member has a personal life too. We don’t live in bunk beds inside the office. Similarly, managers fundamentally enjoy and have a personal life. How would managers feel if staff spent weeks digging years into the past into anything they ever said, even in small private conversations? Or even in public, e.g. the Sirius founder’s Twitter account promoting an insurrectionist, Donald Trump. There seems to be disproportionate selective enforcement and symmetric relationship; the bosses can do anything they want, even violate their own rules, whereas precarious staff is treated as disposable and presumed guilty at all times (e.g. judged based on prejudice and vindication without due process and without regard for access to lawyers, i.e. qualified legal advice). More on that later, for this is a key motivation for this document to put together and carefully crafted with privacy in mind.

Thursday, December 8th, 2022, 4:42 pm

It’s Already December and the British Government Has Decided to Barely Test People for COVID-19

Dec 8 2022 COVID-19

Is the ‘end’ of COVID-19 a political decision, coordinated partly from above by defunding and neglect?

“People tested positive in England,” according to this evening’s numbers (released minutes ago), are numbered at 23,216 for the past week.

Does anyone seriously think so few contracted COVID-19? No. Many of us still know people who not only get infected but also reinfected.

Looking at the lab-based COVID-19 tests conducted (England), here is the number of tests per day:

07-12-2022 7,646
06-12-2022 8,129
05-12-2022 1,758
04-12-2022 3,367
03-12-2022 7,288
02-12-2022 5,034
01-12-2022 10,688
30-11-2022 21,370
29-11-2022 24,782
28-11-2022 21,821
27-11-2022 15,866
26-11-2022 17,892
25-11-2022 19,099
24-11-2022 22,500
23-11-2022 25,377
22-11-2022 25,293
21-11-2022 24,212
20-11-2022 16,051
19-11-2022 17,128
18-11-2022 22,481
17-11-2022 22,791
16-11-2022 25,746
15-11-2022 28,498
14-11-2022 24,824
13-11-2022 15,351
12-11-2022 19,082
11-11-2022 22,427
10-11-2022 24,516
09-11-2022 26,689
08-11-2022 29,500
07-11-2022 25,162
06-11-2022 15,507
05-11-2022 19,275
04-11-2022 25,679
03-11-2022 28,210
02-11-2022 27,450
01-11-2022 31,824
31-10-2022 24,778
30-10-2022 16,980
29-10-2022 22,094
28-10-2022 27,261
27-10-2022 29,453
26-10-2022 32,207
25-10-2022 35,643
24-10-2022 26,232
23-10-2022 20,906
22-10-2022 25,517
21-10-2022 30,388
20-10-2022 34,067
19-10-2022 40,429
18-10-2022 41,373
17-10-2022 30,450
16-10-2022 22,627
15-10-2022 29,966
14-10-2022 33,088
13-10-2022 35,169

Notice how it has fallen to like a quarter what it was just months month ago.

Compare to the first week of December 2021:

07-12-2021 553,722
06-12-2021 486,459
05-12-2021 476,058
04-12-2021 503,124
03-12-2021 585,529
02-12-2021 555,481
01-12-2021 556,367

And the first week of December 2022:

07-12-2020 188,281
06-12-2020 209,309
05-12-2020 265,016
04-12-2020 278,014
03-12-2020 288,355
02-12-2020 262,352
01-12-2020 244,789

Lies, damn lies, and statistics. COVID-19 hasn’t gone away in any meaningful way. We just stopped testing and there’s no prospect of eradication anymore. Excess deaths across England remain very high.

Other testing methods are also down considerably.

Thursday, December 8th, 2022, 9:44 am

Sirius Corporation Threatened With Fines and Penalties for Pension Issues

Video download link | md5sum dd579d8626516657c12134d4acbdec1d
Pensions Provider Unpaid by Sirius
Creative Commons Attribution-No Derivative Works 4.0

Summary: Sirius ‘Open Source’ is unable to cope with basic legal requirements such as sending payslips to staff (this hasn’t been done for months already!) and such issues have gone on for almost 4 years already

THE company I left just less than a week ago had left my wife and I chasing very basic stuff like pensions and payslips. In hindsight, we ought to have left earlier. The company was dysfunctional for years already.

The video above goes through yesterday’s publication, which took a lot of time to piece together as it involved more than 3 years’ (worth of) E-mails and even some photographs of mail. Those were later carefully redacted. In the above video I go through the same using words whilst adding some much-needed context.

Real-time Posts

Posts by @schestowitz

Retrieval statistics: 23 queries taking a total of 0.088 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|