Introduction About Site Map

XML
RSS 2 Feed RSS 2 Feed
Navigation

Main Page | Blog Index

Monday, June 24th, 2013, 11:43 am

TechBytes Episode 78 With Richard Stallman

Richard Stallman on Snowden, NSA, etc.
Techbytes 2013

Direct download as Ogg (00:08:15, 5.9 MB)

Summary: The first part of a series about privacy

TODAY we officially begin a series of interviews with Dr. Richard Stallman, as [cref 69689 promised last week]. Stallman was proven to be right on the issues of privacy and freedom as more information was being shown for everyone to see how surveillance is used to control users’ behaviour and distort/impede communications in some cases. As more evidence came to light, showing in concrete form what a lot of people already knew but could not always prove, there was a lot to be discussed not hypothetically but realistically.

This is the first part of many and the transcript follows (some parts were too incomprehensible due to low recording quality, so we duly apologise for inaccuracies).


Dr. Roy S. Schestowitz: As I said before, I think the plan was mostly to focus on things that we hadn’t touched before and primarily things to do with privacy. I think we were — and many people were — advocating for freedom in technology were proven to be correct in the sense that on the issue of privacy and freedom everything seems to be very symbiotic and I think in recent weeks we found that more and more people have woken up to the fact that they need to assure they can control their software.
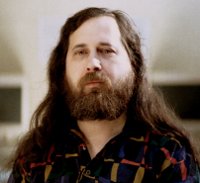
Richard StallmanDr. Richard M. Stallman: It’s not just about what happens in your computer. With Free software you control what happens in your computer, but of course there are other systems of snooping. The NSA is setting up snooping that we have been reading about recently. They don’t work through software in your computer. So, what this shows is, a) they have {users must have} control over the software in your computer; b) we need to work politically to make sure that the software that’s not in our computer — the systems that are not ours — are nonetheless not being used to snoop on us.

RSS: I think information is increasingly being used to change behaviour in people and also to distort the ways of communication between entities and I think that routers, for example, play a role in the way in which we interact with computers, so I wonder what your take is on the [snooping] in routers, many of them [are] Cisco ones.

RMS: Ed Snowden, I think, said that the NSA takes control of routers in order to monitor Internet traffic in other countries.

RSS: It is actually proven to be the case and any interested person who researched this subject before would know that Cisco was working with the Chinese government to enable things like sending E-mail port back to communication and such things, so we do know that there is a degree of collusion between them. I think we’ll touch on this later when we’re just thinking the possibility of back doors. But I think it’s more evident now that it comes to light, showing in concrete terms what we already know was probably happening all these years.

RMS: There are many routers you can get that you can then install free software into. So if we are talking about your router, then yeah, you should put Free software into it. But when you talk to other [incomprehensible] it’s critical to ask first if they are not yours. And some of them will belong to companies that might very well be collaborating with surveillance. And Free software is not going to fix that problem, because if that company which [incomprehensible] for its switch/routers was to collaborate with the NSA, it is going to collaborate with the NSA or the Chinese government or whatever. So, Free software means you can control over the software or what your computer is doing or your computers are doing, but it doesn’t necessarily mean that the other organisations you deal with are going to respect your privacy.

RSS: Unless of course we use encryption, for example.

RMS: Yes. Of course encryption in itself doesn’t disguise who we are talking to and it’s been played out that if the government knows who knows who, then it is a tremendous start on breaking any dissident movement.


The next part will be published in a few days.

We hope you will join us for future shows and consider subscribing to the show via the RSS feed. You can also visit our archives for past shows. If you have an Identi.ca account, consider subscribing to TechBytes in order to keep up to date.

As embedded (HTML5):

Keywords: gnu fsf richardstallman

Download:
Ogg Theora

Friday, June 21st, 2013, 12:30 am

Twitter’s Suicide Plan: Blocking Everything, Again

Twitter is going down the drain and it has itself to blame

Twitter

IMAGINE a company stupid enough to follow the trajectory of MySpace and the now-deceased Digg.com by its very own choice. Enter Twitter.
Twitter was a rapidly-growing site back in the days. It was getting links everywhere, just like Digg had gotten a lot of buttons and links. But then came the OAuth ‘revolution’ and Twitter shot many applications (digital vehicles that brought it traffic) right at the head. It wasn’t an accident. Twitter ended up breaking hooks and denying access by some applications that I was using until 2010, e.g. in IRC. What a colossal mistake. Twitter never quite recovered since then. Au contraire — the site has been declining little by little, especially in recent months. Rather than encourage developers to get involved, Twitter is doing it again — dampening third-party contributions — this time even more aggressively than before.

The news sites took little note of what Twitter had done. Twitter’s API idiocy not only broke crucial parts in 3 Web sites of mine but also in some clients’ sites. Thanks for the trouble, Twitter. You break things and leave us all to collect the pieces.

Twitter is making irrational decisions like killing off RSS, third-party developers, off-site links, etc. Are they on a suicide plan?

Twitter’s own widget, which is apparently what Twitter is trying to promote, is not even valid (X)HTML, so they’re encouraging people to put broken code inside their Web pages while blocking the competition.

Twitter’s future, I would guess, is similar to that of MySpace and Digg.com. The US Library of Congress is saving all the contents, so one day when Twitter.com goes offline we might still remember that old site which committed suicide, taking down with it all of our data, more or less like identi.ca.

Monday, June 17th, 2013, 8:46 am

NatWest: Failing to Call Back (Twice). Succeeding in Illicit Surveillance on Customers?

Prism NatWest

A WEEK ago I asked my bank for clarifications on privacy. The bank manager never called back at all (they had promised s/he would), essentially making promises in vain and evading the serious issue. I contacted NatWest again, expressing disappointment that they broke their promise. An advisor told me they would call back shortly, but I have been waiting for many hours in vain. Here is the chat log:

You are now connected with an adviser.

Guri: Hi, you’re chatting with Guri. How may I help you?

Dr. Roy Schestowitz: Hi Guri

Dr. Roy Schestowitz: Last week I spoke with a Rep. called Manny

Guri: Hi Dr. Schestowitz

Guri: How may I help you today?

Dr. Roy Schestowitz: He spoke to his boss and said they would call me back by Friday

Guri: okay

Dr. Roy Schestowitz: That was a week ago, on Monday

Dr. Roy Schestowitz: He said they would have phoned by the end of the week, but did not

Guri: I am very sorry to hear that…

Guri: may i know regarding what he has arranged the call for you ?

Dr. Roy Schestowitz: I left my telephone number with him, can you please check this?

Dr. Roy Schestowitz: The cal was regarding data privacy in my 5 accounts, I said I would like my data not to be shared across nations.

Guri: May I know the sort code, your full name and first line of address to check the details for you?

Dr. Roy Schestowitz: Sort code: XXXX , Dr. Roy Schestowitz, XXXX

Guri: Thank you. I will locate your details. There may be a slight delay while I check your information. I appreciate your patience.

Dr. Roy Schestowitz: No problem

Guri: Dr. Schestowitz, If you want I will set a new call back for you and you will get the call within 3-4 hours

Dr. Roy Schestowitz: Please.

Guri: May I know your Telephone number?

Dr. Roy Schestowitz: XXXX

Guri: Thank you

Dr. Roy Schestowitz: I look forward to the call in a few hours, thanks and good day

Guri: I have arranged the call back for you

Guri: You will get the call within 3-4 hours

Guri: Is there anything else I can help you with today?

Dr. Roy Schestowitz: That’s all, thanks

it’s not over yet. They failed to call back twice in a row now. I think it’s deliberate because of the nature of the query. They want secrecy around their abuse of customers’ data.

Monday, June 17th, 2013, 8:28 am

Kim Dotcom – The RAID

EVERY NOW and then we’re reminded of the fact that politicians, government, police etc. are driven by corporate interests because money — to them — always comes before principles. Here is how they deal with competition.

Sunday, June 16th, 2013, 12:53 pm

Migration and Upgrading of Techrights

Crows

EARLIER THIS month the server running Techrights got migrated and upgraded (from Linux techrights.org 2.6.18-308.el5xen #1 SMP Tue Feb 21 20:47:10 EST 2012 x86_64 x86_64 x86_64 GNU/Linux with 2 cores on CentOS release 5.9 (Final) to Linux techrights.org 2.6.32-358.el6.x86_64 #1 SMP Fri Feb 22 00:31:26 UTC 2013 x86_64 x86_64 x86_64 GNU/Linux with 4 cores on CentOS release 6.4 (Final)). Thanks go to Copilotco for providing hosting space and kind support. Here is a look at some of the work involved in this whole process. It can be subdivided into a bunch of tasks as follows:

  • Setting up the backup cron job, among other jobs. For the standard user/s this involves just nightly backups of all databases overnight, at around 8 PM East Coast time (the physical server is based in California). For root, the story is a little different. Monitoring is run with E-mail alerts (in addition to third-party services which poll over HTTP and dispatch warnings in Web/E-mail form). Someone wrote a script for automatically restarting Apache and sending some diagnostics around multiple maintainers if the service seems to be malfunctioning. I wonder, however, if we need this to run on the new server by default, considering the fact we might have uptime/continuity of service for months as we did years ago. This used to be run as a cron job, in a line which contains */5 * * * * /usr/local/sbin/web-watch. We will be saving it in the home directory before we decommission the old server and lose data. The scripts associated with the jobs have been copied and given the same permissions as before, so they should be usable. HTTPD restart script (in cron job with correct permissions in associated files) requires some cold testing, with additional cron jobs-related tests (requires lots of testing to prevent major catastrophe, e.g. .htaccess should not be (mis-)configured to permit access to privileged parts of the site (none except system files)).
  • Needing to compare DB sizes to assure all data was migrated successfully (about 1.8 GB of text in the databases). This is tricky for a tool like diff to address. Given that the import yielded no warings and the database dump sizes are roughly right (with the newer, active database being slightly larger), this seems to be passing the sanity check. Readers were encouraged to report problems with the site, as well.
  • Blocking wiki edits which are anonymous, i.e. from the new address of Varnish. There are Wiki spamming attempts ongoing, and as soon as new registrations and edits by them are allowed, the Wiki gets littered with spam. None of that has stopped.
  • Merging of domains is work in progress. In Google, site:http://boycottnovell.com might start showing duplicates (w.r.t. Techrights.org) because access to the former domain does not result in the URL being overwritten/rewritten as Techrights.org. To prevent the search engines’ indexes from filling up for two separate domains, the old behaviour is preferred and should be restored. In short: Needing to check that all domains, two .com domains and the default .org domain, are all merged properly to give one single URL for each page, with no plurality (canonical form). Testing a lot of pages on different kinds of sites/domains, redirections included, e.g. boycottnovell.com/SOME-POST-PATH, helps provide reassurance here (for link integrity, i.e. no 404s, not just SEO-driven).
  • Finding the master template for /etc/sudoers, wherever it resides. We need to add a line to sudoers to allow for faster restarting of the IRC bot/s.
  • The statistics package we use (needed for security with 4-week retention, but locally-accessible only, for privacy reasons), a simple program called Visitors, has been recompiled for the new server and data passed to /root where scripts reside whose function is retained, having replicated Apache configurations and other settings that relate to them. Some testing is still required for some bots’ function, e.g. access via HTTP to localhost. The Varnish proxy complicates debugging.
  • Checking of cache directories and plugins, ensuring that they work and aid performance. Pages should generally be loaded more quickly, owing in part to hardware improvements.
  • IRC logs and access to them should be verified (5 years’ worth), along with access to directories through contents listing (blocked by default in some Apache configurations). Seeing errors through logs can help diagnose such issues.
  • MIME types for filetypes such as Ogg should be checked, with different file extensions and in-page embedding being tested. A test of oggs seems mostly fine, at least for TechBytes episodes. On the old server (under /etc/mime.types), “video/ogg ogg ogv ogm” was used to capture variations of file extensions. The new server needed OGM added (cat /etc/mime.types | grep ogm showed it to be conspiciously missing).
  • Mailing technical details to another privileged user, perhaps getting another public key on the server.
  • Magpie RSS in the Wiki for fetching latest stories from WordPress. Currently, this does not work and it did prove problematic in the past, too.
  • There are 4 directories of Patent Troll Tracker posts which need to be made inaccessible (chmod 000 for instance) as the author asked them to be made invisible (he got sued over it) before we made the mirror. This is needed for offline preservation (information about notorious patent trolls).
  • Needing to recheck root directories for similarities, ensuring nothing valuable is left behind on the decommissioned server. This can be achieved most simply using a count of files in several locations, checking space used in areas of importance.
  • Directory listings, e.g. listing of court exhibits, should be enabled despite the default paranoid setting in Apache. Alternative domain names will inherit those same rules if properly set up.
  • Resorting a regular remote backup routine, e.g. through the gateway or from server directly to desktop (in the UK), in addition to backups near the rack.

Monday, June 10th, 2013, 1:56 pm

Ask Your Bank to Stop Giving Your Bank Details/Data/Purchases to Spooks Abroad

Prism NatWest

WITH PRISM all over the news, politicians in Finland (land of Nokia) are being pressured to drop E-mail services that give the US data which compromises sovereignty, e.g. political espionage.

Contributing my own bit to this push for sovereignty, I have contacted my bank, National Westminster, which will probably tell me I can’t opt out of sending my financial data to the US, land of illegal surveillance by NSA. I am now waiting for a phonecall from someone higher up in National Westminster. Here is my chat log from an hour ago:

Manny: Hi, you’re chatting with Manny. How may I help you?
Dr. Roy Schestowitz: Hi Manny, good afternoon.
Manny: Good Afternoon
Manny: How can I help today?
Dr. Roy Schestowitz: I have 5 accounts with NatWest, 1 of which is a USD account
Dr. Roy Schestowitz: Several months ago I contacted NatWest regarding my newly-issued debit card, which is tied to Visa, not Maestro/Switch
Dr. Roy Schestowitz: I had asked them to stop sending my financial data to Visa
Dr. Roy Schestowitz: I wish to use my account without going through a foreign party
Manny: Okay, is that for your USD account, or the regular account?
Dr. Roy Schestowitz: All accounts preferably
Dr. Roy Schestowitz: I want my financial data to stay within the UK, I think the law protects me on this matter
Dr. Roy Schestowitz: I can give my account details if they helps
Manny: Okay, do you do online banking with your accounts?
Dr. Roy Schestowitz: Yes, I do
Manny: Okay, can you log in online for me please?
Dr. Roy Schestowitz: The USD account I cannot access online, it’s a Currency Account, but it’s based on Warwick, if I recall correcly, so I assume the data stays in the UK
Manny: Okay, can you log in online for me please?
Dr. Roy Schestowitz: Sure, hang on..
Dr. Roy Schestowitz: I am logged in now
Dr. Roy Schestowitz: By the way, the chat facility did not work in Firefox
Dr. Roy Schestowitz: Maybe a bug, I had to launch Chromium to get to it
Manny: Thank you, okay, and what is it you would like me change on the account exactly please?
Dr. Roy Schestowitz: My accounts are, based on information I have been given by NatWest, enable my financial activity to be sent to another nation, even when I make payments within the UK
Dr. Roy Schestowitz: I would like to opt out
Manny: Okay, one moment please.
Dr. Roy Schestowitz: thank you, Manny
Manny: Okay, we wouldn’t share an specific financial information with any parties outside of the UK, and any monitoring on your account or Visa card, would be done solely by the bank, and no one else.
Manny: I haven’t heard from you for a while. Are you still there?
Dr. Roy Schestowitz: yes
Manny: Is this in reference to making payment via the internet or just using your card in general anywhere?
Dr. Roy Schestowitz: I am trying to interpret this because it’s sufficient for the processing to be done by Visa for another nation to hold a copy of all transactions
Dr. Roy Schestowitz: Using my card as well as making transaction over the Internet. I need reassurance that in both cases the financial data is in no way trickling out outside the UK.
Dr. Roy Schestowitz: That would contradict what NatWest told me before, as they said Visa is a “man-in-the-middle” in the transactions
Manny: Okay, I don’t have access specifically to that information here I’m afraid, Dr. but what I will do for you is, send this on for investigation, and then my supervisory will look into this situation further for you, and then call you back once all the necessary information has been located for you.
Manny: You will get a call back within 5 working days at the very latest, is that okay for you?
Dr. Roy Schestowitz: Thank you, Manny
Manny: You’re very welcome, may I take your best daytime contact number please?
Dr. Roy Schestowitz: I am at home most of the time, the number to reach me on is xxxxxx
Manny: Thank you, I will get this request send for you right away, and you will hear back within 5 working days.
Manny: Is there anything else I can help you with today?
Dr. Roy Schestowitz: That’s enough for today, thank you. I shall wait for the call for clarifications, I hope they can amend my accounts to address the privacy problems that I never opted into
Manny: Okay, not to worry.
Manny: I would be grateful if you could take a moment of your time to complete the attached survey in connection with the service I have provided today?
Manny: Thank you for chatting with me. I hope you enjoy the rest of your day.

Stay tuned…

Wednesday, May 29th, 2013, 4:35 pm

Google Glass: Wearable Surveillance

1411835_the_live_food_

OTHER than the fact that Google Glass is Linux-powered and partly Free/Open Source, I have never had interest in Google Glass. The fact that it is hackable — in the sense one can install one’s own system on the hardware — sure makes a difference, but most people will never practise this freedom. As long as Google, by default, hoovers in data from Google Glass (like it does on the Nexus series), the data is easily accessible to the Surveillance Industrial Complex. This ties into the previous post about peer-surveillance. There is no escaping it and there is reason to antagonise Google Glass as a concept, irrespective of whether one buys/uses it. A lot of people will have no choice as to whether their life(as dynamic imagery) is taken and then uploaded to a datacentre with weak data sharing/protection/retention policy. This is not the same as CCTV. Here we talk about videos that are captured in private spaces, too, more so than surveillance drones whose motion is limited to aerial and is still privacy-infringing, albeit they’re less ubiquitous due to cost, air traffic control, legislation and so on.

This is not about resisting a brand. It’s not hating advancement or fearing the future as Google likes to paint it. It is about telling the difference between marketing (the technology for Google Glass as an implementable concept has been around for decades) and societal effects. It’s like antagonising proprietary software for its effects on society, regardless of practical uses. Fog Computing (‘cloud’) should be rejected on similar grounds. Not everything that can be done should be done, at least or especially if it disregards the consent of non-participants.

To the user, the novelty here is the size of the hardware, the image resolution, and the wireless connection speeds (not related to Google at all).

To the Surveillance Industrial Complex, the novelty here is the ability to access a private (i.e. not accessible by us) database of videos for any given person queried (identity can be derived in a variety of ways, ranging from inter-personal connections to audio, video, and geographical location).

Real-time Posts

Posts by @schestowitz

Retrieval statistics: 23 queries taking a total of 0.095 seconds • Please report low bandwidth using the feedback form
Original styles created by Ian Main (all acknowledgements) • PHP scripts and styles later modified by Roy Schestowitz • Help yourself to a GPL'd copy
|— Proudly powered by W o r d P r e s s — based on a heavily-hacked version 1.2.1 (Mingus) installation —|